Core Lightning, one of the prominent software implementations used for running Bitcoin Lightning Network payment nodes, has officially released version v26.06.9. This latest software update introduces crucial security patches, alongside a targeted repair for a performance regression that had the potential to throttle channel traffic on heavily utilized, busy nodes running the immediately preceding v26.06.8 release.
According to repository updates listed on GitHub, the new release was published on Oct. 7, while its accompanying versioned changelog carries an Oct. 6 publication date. For network operators who recently installed v26.06.8, this latest patch provides a fresh evaluation point for upgrading their infrastructure. This comes closely on the heels of a significant security incident on Sept. 27, when a revoked-channel penalty flaw was discovered and subsequently patched in version v26.06.7. The newly deployed v26.06.9 update not only builds upon those foundational security adjustments but also systematically addresses a regression that was inadvertently introduced during the earlier patch cycle.
Bitcoin Payment Delays and Channel Shutdown Risks
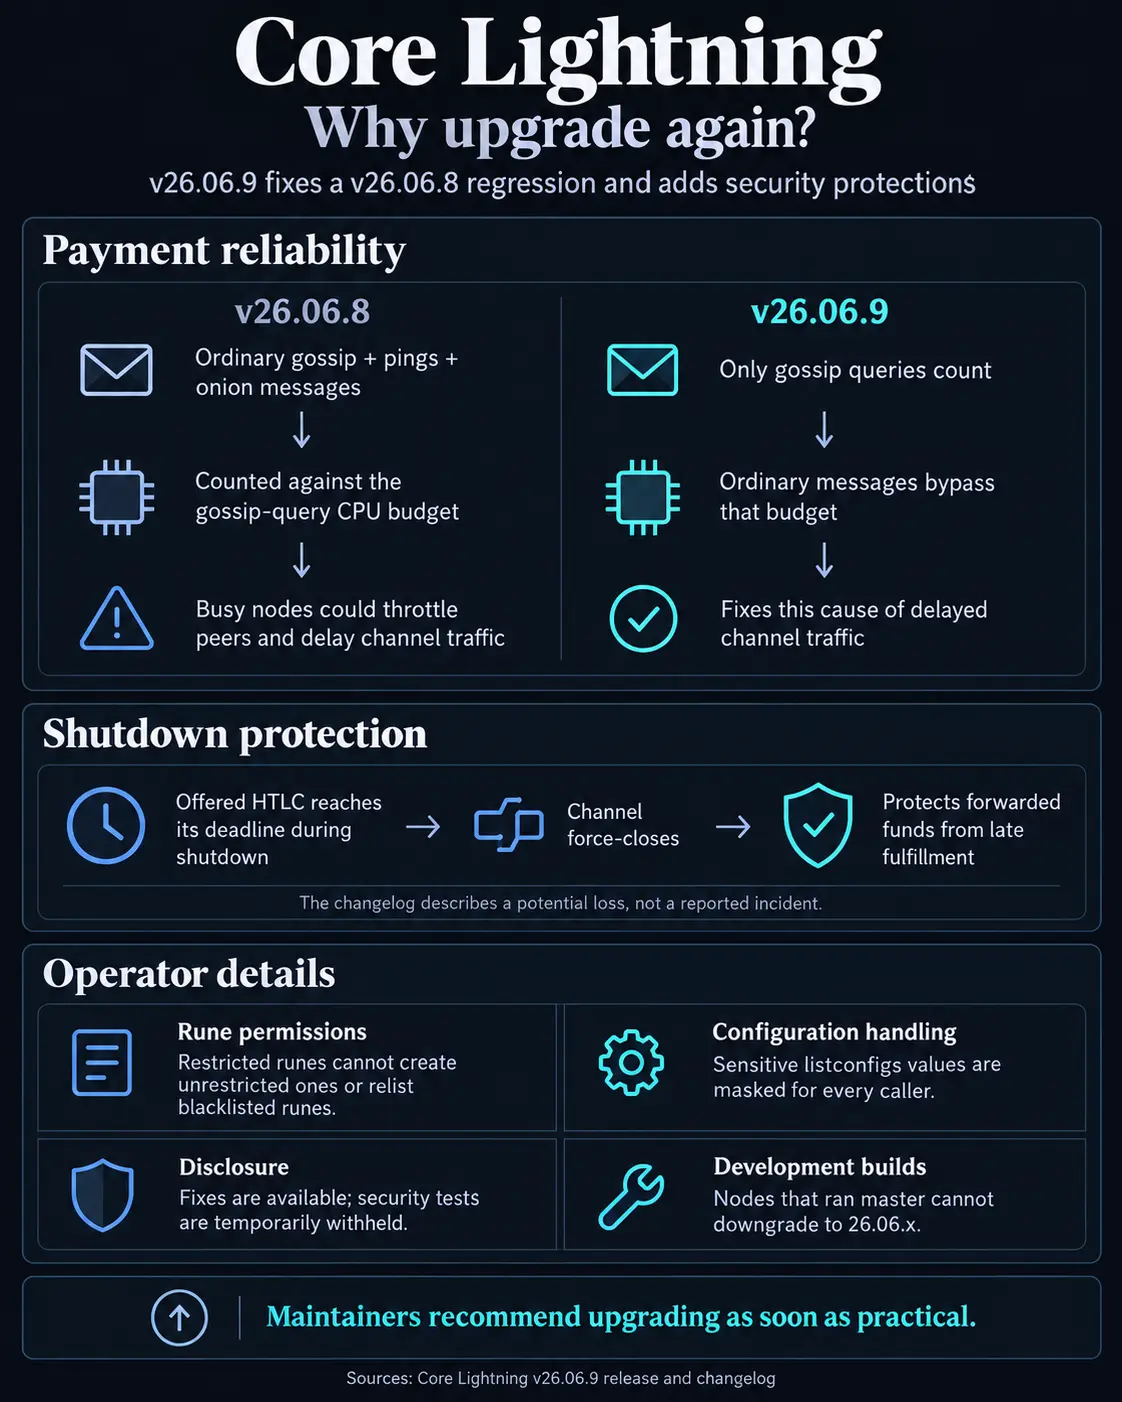
The motivation behind the swift deployment of v26.06.9 stems from specific operational bottlenecks and risk factors identified by maintainers in the previous iteration. In Core Lightning v26.06.8, routine network operations such as gossip exchanges, pings, and onion-routed messages were incorrectly factored into a CPU budget originally designed exclusively for gossip queries. On high-volume, busy nodes handling substantial transaction throughput, this accounting oversight meant that standard background messages could end up throttling peer connections, thereby introducing noticeable delays to active channel traffic.
With the release of v26.06.9, developers have restructured the software’s resource allocation so that the CPU budget is strictly reserved for genuine gossip queries. Ordinary network messages no longer draw from this restricted pool, effectively eliminating the root cause of the traffic throttling reported by operators of busy nodes running the v26.06.8 software.
Beyond performance and traffic management, the changelog highlights a critical fix concerning payment contracts, specifically Hash Time-Locked Contracts (HTLCs), that reach their absolute deadlines precisely while a channel is in the process of shutting down. Under previous conditions, an overlapping timeline between a maturing payment contract and a channel closure could create severe settlement vulnerabilities. Version v26.06.9 resolves this by enforcing a mandatory force-close of the channel in such scenarios. This procedural adjustment ensures that forwarded funds are fully protected and shielded from potential loss if a time-sensitive payment is fulfilled late in the shutdown sequence. For professional node operators who actively forward payments across the Lightning Network, this modification closes a vital loophole regarding fund security during complex network states.
Security Enhancements, Permission Controls, and Configuration Safeguards
In addition to resolving traffic regressions and shutdown risks, the v26.06.9 release implements several robust security measures to protect node operators against unauthorized access and configuration injection. The software now strictly enforces the specific permission limits carried by runes—the authorization tokens used to make remote procedure call (RPC) requests. Under the updated rules, a restricted rune is blocked from creating an unrestricted counterpart, and it can no longer be used to relist blacklisted runes. Furthermore, security restrictions governing the creation and blocklisting methods have been systematically expanded to cover the invokerune and destroyrune aliases, closing potential privilege escalation vectors.
Operational visibility and administrative security have also been tightened. The listconfigs command has been modified to automatically mask a variety of sensitive configuration values, including internal recovery information and underlying Bitcoin RPC passwords, for every caller regardless of permission level. Concurrently, the setconfig command has been updated to close a previously identified vulnerability that could allow malicious actors to inject arbitrary configuration lines through persistent option values.
Deployment Guidelines and Operational Considerations
The patches and enhancements included in v26.06.9 are available immediately to the global Bitcoin and Lightning Network community. However, in a deliberate move to safeguard the network during the adoption phase, maintainers have temporarily withheld the release of associated security tests. This strategic delay is intended to make exploit development significantly harder for malicious actors, thereby granting node operators a safer, extended window of time to perform necessary infrastructure upgrades.
Maintainers have also issued important technical advisories regarding database compatibility and experimental features. Nodes that have already been updated to run the development master branch cannot downgrade to any release within the 26.06.x family, as the underlying database schema has advanced beyond older versions. Additionally, the release notes reiterate that dual funding functionality remains experimental within the codebase and strongly discourage the use of zero-confirmation channels when interacting with untrusted or unverified peers.
Given the combination of traffic optimization fixes, critical funds-protection mechanisms, and essential security hardening, maintainers are strongly urging all Core Lightning users—including those currently operating on version v26.06.8—to upgrade their nodes to v26.06.9 at their earliest practical convenience.