Security teams across enterprises are finding themselves trapped in a paradox of high activity and stagnant risk. Organizations are remediating more vulnerabilities than ever before, yet their overall breach risk has barely moved. Security professionals spend countless hours and substantial resources addressing exposures that attackers may never exploit, while genuine, high-risk vulnerabilities sit neglected in sprawling backlogs. According to recent research highlighted in Gartner reports on exposure prioritization, fewer than 10 percent of known vulnerabilities are ever actually exploited in the wild, yet the vast majority continue to be treated with emergency urgency. Furthermore, industry experts argue that relying solely on Common Vulnerability Scoring System (CVSS) metrics fails to accurately predict real-world exploitation or genuine business impact.
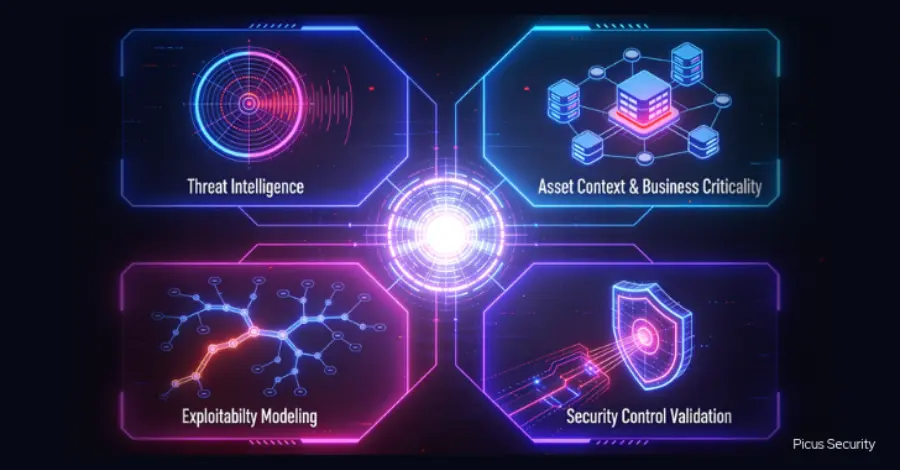
To address this systemic industry challenge, Gartner has issued a bold prediction. By the year 2028, organizations that pivot away from traditional, CVSS-centric vulnerability prioritization and instead adopt advanced exposure management frameworks will slash their breach likelihood by at least 70 percent compared to their peers. This modern framework relies on four foundational pillars: comprehensive threat intelligence, deep asset context, advanced exploitability modeling, and continuous security control validation. Industry technology providers, such as the Picus Platform, have increasingly focused on operationalizing these four critical elements to transform how enterprises tackle modern attack surfaces.
The reliance on severity-based prioritization was entirely rational for the technological era in which it was conceived. Decades ago, organizations operated within a relatively static attack surface, adversary tooling was scarce, and internal remediation capacity routinely outpaced the volume of newly disclosed vulnerabilities. However, that world has completely vanished. Modern enterprises now grapple with tens of thousands of new vulnerabilities annually spanning complex cloud environments, software-as-a-service applications, identity systems, and intricate supply chain modalities. Moreover, the emergence of advanced automation and artificial intelligence has dramatically compressed the time-to-exploit window from weeks or months down to mere hours.

Industry observers note that security teams do not anchor on severity scores out of a simple lack of awareness. Rather, traditional corporate structures, regulatory frameworks, and compliance mandates heavily reward what is easily auditable over what delivers legitimate, measurable risk reduction. The inevitable consequence of this compliance-driven approach is widespread prioritization paralysis. Significant capital and operational resources are funneled into patching low-risk issues simply because they carry high severity numbers, leaving organizations with little tangible risk reduction to show for their efforts.
The smarter path forward requires embracing risk-based vulnerability management in its truest form. Organizations must measure their security success by the reduction of genuinely exploitable exposures rather than the accumulation of closed hypothetical vulnerabilities. Gartner’s strategic framework establishes that true exposure management rests on four distinct pillars, and their collective value only emerges when they are integrated into a single cohesive process. While operationalizing one or two of these elements can yield incremental operational gains, combining all four delivers dramatic reductions in exposure windows and significantly alleviates chronic remediation fatigue.
Each of these four foundational elements answers a specific, vital question about any given security exposure. Threat intelligence addresses whether active adversaries care about the vulnerability. Asset context evaluates the business criticality of the targeted system. Exploitability modeling estimates the statistical probability that the vulnerability will be weaponized. Finally, security control validation tests whether existing defenses can successfully block an attack chain in the organization’s unique environment. An exposure warrants urgent, top-tier remediation only when the answers across all four categories converge to confirm a genuine and present danger.
This model aligns directly with the continuous threat exposure management lifecycle, ensuring that operational remediation is mobilized only after priorities have been rigorously validated in context. Threat intelligence brings the adversary’s perspective directly into the prioritization equation by revealing which specific exposures attackers are actively leveraging in real-world campaigns. In practice, many high-severity vulnerabilities are frequently ignored by threat actors, while moderately rated flaws are heavily weaponized because they are easier to exploit or provide reliable access to widely deployed systems. Past exploitation evidence allows security teams to narrow their focus to a much smaller, highly dangerous subset of their total vulnerability backlog.

However, operationalizing threat intelligence requires exceptional speed. Security teams must ingest threat data rapidly to determine what needs to be tested and fixed long before an active adversary campaign reaches corporate perimeters. Beyond knowing what attackers are targeting, organizations must understand the value of the assets under attack. An exploitable vulnerability becomes materially critical only when it resides on a system that supports core business functions, handles regulated data, or offers an easy lateral movement path to higher-value network segments. Without proper asset context, prioritization treats all servers, endpoints, and cloud instances as equally important, allowing attention to drift toward low-impact systems while crown-jewel assets remain exposed.
This critical context typically resides across disparate tools already owned by the enterprise, including vulnerability scanners, configuration management databases, cloud security platforms, and identity management systems. The practical challenge for security operations is unifying these data sources and keeping them continuously updated so that asset criticality reflects the environment as it is defended today, rather than how it appears on an outdated network inventory.
To complement threat intelligence and asset context, exploitability modeling tools such as the Exploit Prediction Scoring System attempt to estimate the likelihood of a vulnerability being weaponized. These predictive models analyze historical patterns, including exploit complexity, component prevalence, and the timeline between disclosure and exploitation. By surfacing latent risks, statistical models help security teams identify exposures that are likely to be exploited before widespread attacks are publicly observed, fostering a more anticipatory security posture.
Nevertheless, statistical likelihood describes the broader threat landscape in general terms rather than an organization’s unique environment. Predictive models point to what is probably exploitable somewhere in the global ecosystem, but only active validation can prove what remains exploitable within a specific corporate network. Therefore, exploitability modeling functions best as an intelligent filter that feeds into security control validation rather than serving as a definitive final verdict.

Security control validation represents the missing link in the vast majority of enterprise vulnerability management programs. This pillar evaluates each exposure against the specific defensive layers already deployed around it, such as network segmentation, endpoint protection platforms, runtime monitoring, and identity controls. An exposure that appears catastrophic on paper may be completely unreachable behind robust, properly configured defenses, whereas a lower-scored vulnerability on an unmonitored asset could present an existential threat. Ignoring control context inevitably leads to a systematic overestimation of organizational risk and drives the wasted remediation efforts that plague modern security teams.
By utilizing adversarial exposure validation techniques, organizations can prove or disprove exploitability with empirical evidence through safe live attack execution and attack-chain analysis. When enterprises bring threat intelligence, asset context, exploitability modeling, and security control validation together into a unified, continuous loop, vulnerability management successfully matures into true exposure management. Led by security research and engineering efforts at firms like Picus Security, modern platforms are increasingly designed to automate this convergence, helping enterprises navigate the shift from reactive patching to evidence-based risk decision-making.