
Cybersecurity researchers have detected active exploitation attempts targeting a critical security flaw in OpenSSH just hours after its public disclosure. The vulnerability, which has been […]
Tag: severity
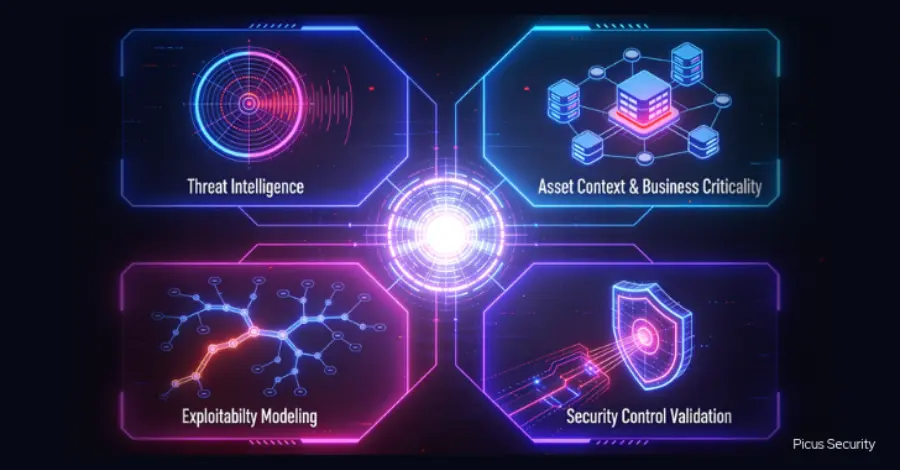
Gartner Predicts Threat-Driven Exposure Prioritization Will Cut Breach Risk by 70% as Severity-Based Models Falter
Security teams across enterprises are finding themselves trapped in a paradox of high activity and stagnant risk. Organizations are remediating more vulnerabilities than ever before, […]
Critical Maximum-Severity Vulnerability in CryptoPayment Gateway WordPress Plugin Actively Exploited
By Ravie Lakshmanan | November 03, 2026 Threat actors have begun actively attempting to exploit an unpatched, maximum-severity security vulnerability in the CryptoPayment Gateway WordPress […]
Critical Maximum-Severity Vulnerability in Siemens SIMATIC IoT2050 Advanced Devices Under Active Exploitation
A maximum-severity security flaw impacting Siemens SIMATIC IoT2050 Advanced hardware running Industrial OS with Node-RED installed has officially come under active exploitation in the wild, […]
Tens of Thousands of Attacks Target High-Severity RCE Flaw in WordPress Core Shortly After Patch Release
By Ravie Lakshmanan October 30, 2026 Threat actors have swiftly mobilized to exploit a high-severity security vulnerability affecting WordPress Core, launching tens of thousands of […]
TeamViewer Fixes High-Severity Flaw Allowing Remote Hosts to Attack Connecting Controllers
TeamViewer has rolled out a critical security update to address a high-severity vulnerability that effectively flips the script on remote desktop sessions, allowing a compromised […]