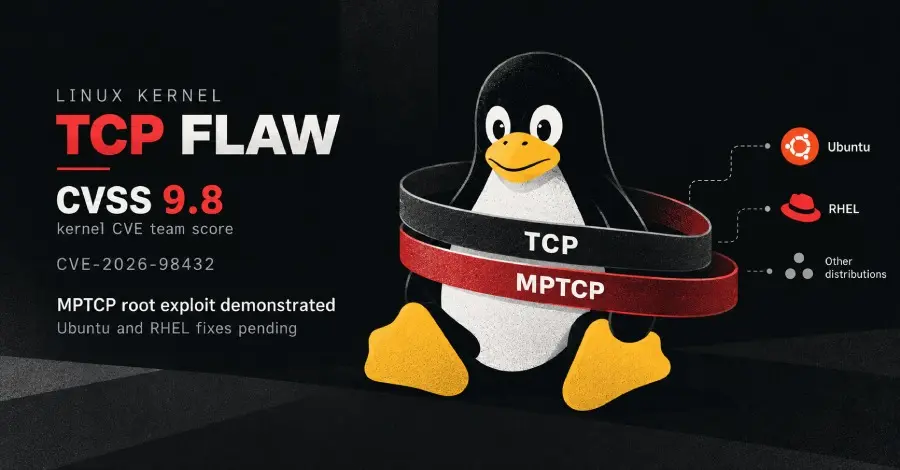
A severe security vulnerability residing deep within the networking architecture of the Linux kernel has come to light, threatening a wide array of enterprise Linux distributions including Ubuntu and Red Hat Enterprise Linux. Tracked under the identifier CVE-2026-98432, the flaw targets the kernel’s Transport Control Protocol (TCP) code. The internal CVE team managed by the Linux kernel developers has assigned the vulnerability a maximum severity rating of 9.8 out of a possible 10 on the Common Vulnerability Scoring System (CVSS) scale, categorizing it as a critical hazard for server infrastructure worldwide.
The gravity of the situation was underscored when AI research firm Anthropic announced on October 27 that its artificial intelligence model had successfully written a fully functional exploit targeting the vulnerability. According to the company, the AI-generated exploit allows an unauthenticated, remote attacker to execute arbitrary shell commands with root privileges on Linux servers equipped with a multipath TCP listener.
As the security community scrambles to understand the implications of automated exploit generation combined with a low-level kernel bug, major enterprise vendors are moving at differing speeds to patch their systems. As of October 29, heavily utilized distributions such as Ubuntu and Red Hat Enterprise Linux (RHEL) had yet to release updated kernel packages containing the fix. Furthermore, prominent technology vendors including Red Hat, Amazon, Oracle, and SUSE have assigned varying CVSS ratings ranging between 5.9 and 8.1, notably lower than the maximum 9.8 score attributed by the kernel team.
How the Underlying Use-After-Free Bug Works
The vulnerability itself stems from a classic race condition embedded within the code responsible for establishing new IPv4 TCP connections. Specifically, the flaw occurs during the intricate TCP handshake process. When a connection request is successfully completed, the Linux kernel hands the Internet Protocol options—which are stored alongside the pending connection request—directly over to the newly minted socket without taking the time to duplicate them.
If that particular socket is subsequently destroyed while another Central Processing Unit core is still actively utilizing those IP options to respond to a retransmitted connection request, the kernel attempts to read memory that has already been deallocated and freed. This particular software bug pattern is widely recognized in cybersecurity circles as a use-after-free vulnerability.
Interestingly, IPv6 connections remain unaffected by this specific race condition because the kernel explicitly copies the necessary options for IPv6 traffic rather than passing references. Code repository records indicate that the bug was originally introduced into the Linux codebase way back in version 4.4. Kernel developers ultimately applied an upstream fix on October 5, roughly ten days before the vulnerability was officially assigned a CVE identifier. The remediation requires the kernel to wait patiently until all other CPU cores finish reading the relevant options before any memory is freed.

The bug fix officially credits Anthropic researcher Xinyang Ge with reporting the vulnerability to the upstream maintainers. While the official CVE record and the kernel commit patch do not explicitly mention multipath TCP, the direct connection between that specialized networking feature and the vulnerability was revealed in Anthropic’s public disclosure. Multipath TCP, or MPTCP, is a feature that allows a single transport connection to utilize multiple network paths simultaneously, though Linux applications must explicitly request MPTCP when opening a socket.
Conflicting Severity Scores Across the Industry
The immense disparity in how major Linux vendors score CVE-2026-98432 has drawn significant attention from enterprise administrators trying to prioritize their patching schedules. The Linux kernel’s CVE team added the 9.8 severity score to the official record on October 24, calculating that an attacker sending an initial TCP connection request with IPv4 Record Route or Timestamp options—followed by a retransmitted request to win the race condition—could trigger memory corruption, leak nearby kernel memory, or crash the operating system entirely. The kernel team classified the attack complexity as low because both sides of the race condition are triggered externally.
Conversely, Red Hat initially rated the flaw as Moderate with a score of 5.9 on its public CVE page, arguing that winning the race condition is difficult in practice and that the most probable outcome is a simple kernel crash rather than remote code execution. However, Red Hat’s internal machine-readable advisory files and bug trackers subsequently updated the severity assessment to Important with a CVSS score of 8.1, acknowledging potential high impacts on both data confidentiality and system integrity.
Other major distributors have similarly aligned with the 8.1 score. Oracle and SUSE both rate the vulnerability as Important with an 8.1 score, mirroring the vector metrics utilized by the kernel team with the sole exception of rating attack complexity as high rather than low. Amazon has assigned the vulnerability a score of 7.0 across its relevant packages. Meanwhile, the National Vulnerability Database had not yet published its own independent analysis, defaulting to the kernel team’s 9.8 score, which is also reflected on Ubuntu’s advisory pages.
Anthropic’s Demonstration of Automated Exploit Chains
Anthropic’s disclosure detailed how its unreleased AI model, Claude, managed to construct an end-to-end exploit chain following initial prompting. The resulting exploit operates in two sophisticated stages. In the first phase, the race condition forces the kernel to leak extra bytes of data back to the attacker. Once a leaked reply contains a valid kernel memory address, the attacker can successfully bypass Kernel Address Space Layout Randomization (KASLR), a core defensive security measure designed to randomize memory locations.
During the second phase, the identical bug is leveraged to trigger a buffer overflow, overwriting a critical callback pointer with the memory address of a malicious payload that the attacker has already positioned within kernel memory. When the kernel subsequently invokes that pointer, the payload executes arbitrary shell commands with full root privileges. Anthropic noted that a failed race condition merely drops that specific connection attempt without crashing the entire operating system, enabling an attacker to continuously retry the process. In their testing environment, leaking a kernel address took roughly 48 minutes, while achieving complete command execution required an additional five minutes.

Despite the technical sophistication demonstrated by the AI model, no active exploitation of CVE-2026-98432 in the wild has been documented by vendor advisories, the CVE record, or intelligence catalogs maintained by security agencies as of late October.
Patch Status Across Major Linux Distributions
The availability of software updates varies significantly depending on the specific Linux distribution utilized by enterprise environments. Debian, Oracle Linux, SUSE, and Amazon Linux have successfully released fixed kernel packages for their stable distributions. Oracle issued fixes through its Unreleased Enterprise Kernel updates as early as October 16, while Debian patched its stable trixie and bookworm releases across mid-October. SUSE has rolled out updates for openSUSE Leap and Linux Micro, and Amazon Linux 2023 has patched several of its kernel packages.
However, organizations relying on Ubuntu and Red Hat Enterprise Linux face a waiting game. Ubuntu has confirmed that work on fixed kernels for versions including 22.04 LTS, 24.04 LTS, 26.04 LTS, and 26.10 is currently in progress, though older releases like 16.04, 18.04, and 20.04 remain vulnerable with no patches currently scheduled. Red Hat stated that its security updates for RHEL versions 8, 9, 10, and OpenShift 4 have been deferred to future updates, with neither vendor providing a definitive release date for the patches.
Administrators managing custom-built kernels are advised by the kernel CVE team to upgrade directly to the latest stable branch releases where the upstream fix has been backported, such as Linux versions 5.10.272, 5.15.223, 6.1.190, 6.6.159, 6.12.113, 6.18.56, 7.2.10, 7.3, and later. The kernel security community strongly discourages cherry-picking isolated patches manually, recommending complete environment updates to ensure system stability and comprehensive protection against the vulnerability.