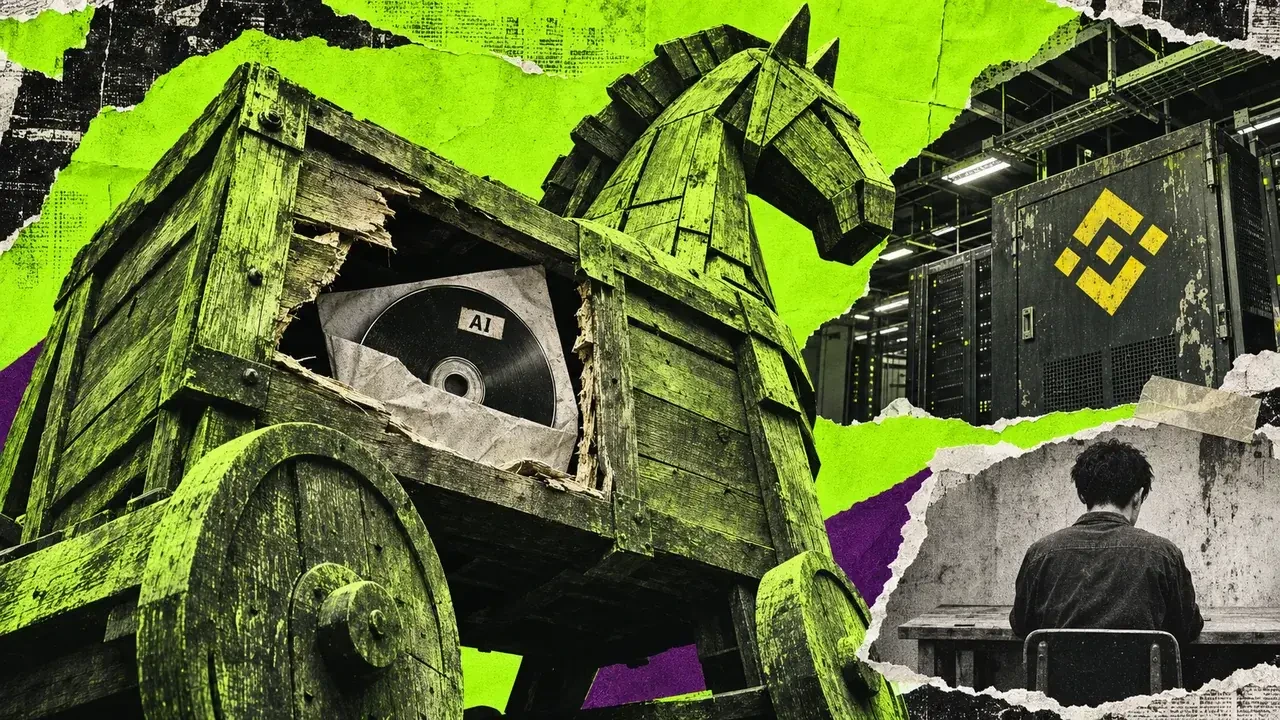
Cryptocurrency exchange Binance has disclosed that hackers successfully exploited its internal artificial intelligence tools to compromise key engineering personnel before executing a massive theft of $6.34 billion in digital assets.
In its comprehensive security report released on Nov. 3, Binance detailed how the malicious actors leveraged a compromised employee computer alongside an internal AI tool on Oct. 20. This breach allowed the attackers to take control of two specific engineers who were directly responsible for managing the platform’s core wallet infrastructure.
With this level of unauthorized access achieved, the attackers subsequently obtained a container deployment permission token. This critical credential acquisition enabled them to penetrate the exchange’s wallet-signing operations on Oct. 29, ultimately allowing them to initiate and execute unauthorized transactions across multiple distinct blockchain networks.
This shocking disclosure places artificial intelligence squarely at the center of one of the largest cryptocurrency thefts recorded in history. The incident significantly amplifies growing cybersecurity concerns regarding how increasingly interconnected AI systems within corporate environments can inadvertently introduce severe, novel vulnerabilities into critical infrastructure.
Binance’s internal investigation has noted that the findings do not establish that an AI model autonomously planned or executed the massive theft. Rather, the attackers weaponized and exploited an existing internal AI tool as a strategic component within a much broader, highly sophisticated campaign. This multi-stage operation relied heavily on stolen credentials, compromised developer software, and targeted social engineering tactics.
The groundwork for the catastrophic breach was laid months in advance. In June, a Binance engineer inadvertently downloaded a tampered software installer while attempting to install a popular AI coding tool. Although Binance’s security mechanisms detected the suspicious activity at the time—prompting the company to replace the affected device and rotate all associated credentials—critical information regarding the targeted employee and their colleagues had already been exposed to the threat actors.
By September, another Binance engineer fell victim to a separate, elaborate fake recruitment operation. This ploy involved meticulously staged job interviews paired with a malicious coding assignment. The hidden malware successfully compromised the employee’s computer, granting the attackers a persistent foothold which they later leveraged to move deeper and more destructively into Binance’s internal enterprise systems.
Following the extensive breach and initial analysis, the Federal Bureau of Investigation (FBI) has formally attributed the broader attack campaign to North Korea. State-backed hacking operations originating from the region have increasingly focused their aggressive cyber activities on software developers, tech personnel, and cryptocurrency enterprises worldwide.
AI Becomes a Growing Weapon in Cyberattacks
The devastating Binance incident arrives on the heels of months of urgent warnings from cybersecurity researchers and threat intelligence firms, who have repeatedly cautioned that the rapid expansion of artificial intelligence is simultaneously broadening hackers’ operational capabilities and the attack surface of enterprise systems.
In February, Google’s Mandiant division reported that North Korean threat actors targeting the global cryptocurrency industry had systematically incorporated AI-assisted techniques into their day-to-day operations. The researchers meticulously documented a sophisticated intrusion involving a fake video conference, malicious software, and a suspected AI-generated video designed to impersonate a high-ranking corporate executive. While researchers could not independently verify the deepfake in that particular specific incident, they clearly identified the group’s utilization of advanced AI tools for reconnaissance and targeted social engineering.
As the year progressed, Google’s Threat Intelligence Group reported in September that malicious actors were moving far beyond simply using AI to generate deceptive content. Instead, attackers were transitioning toward fully automated operations capable of executing multiple complex stages of an enterprise intrusion with minimal human intervention.
In one observed case, hackers successfully compromised a cloud resource and rapidly orchestrated an AI-assisted mass credential-harvesting campaign in less than six hours. Furthermore, Google identified threat actors actively attempting to manipulate AI-powered coding assistants and automated security scanners during complex software supply-chain compromises.
These chilling findings closely mirror a critical aspect of the Binance breach: software developers and the increasingly sophisticated, AI-powered tools they depend on for daily productivity are rapidly becoming the primary vectors attackers use to bypass perimeter defenses and reach deeply sensitive corporate systems.
In a related disclosure last September, AI developer Anthropic revealed that both opportunistic cybercriminals and suspected state-sponsored operators had utilized its Claude models to conduct reconnaissance, develop custom exploitation tools, and automate large-scale data theft. Certain operations reportedly involved autonomous AI agents carrying out multi-stage attacks with minimal human supervision, effectively lowering the technical expertise and manpower traditionally required for enterprise-grade breaches.
Binance Turns to AI Companies to Strengthen Security
In the wake of the historic breach, Binance is actively seeking strategic support from the very technology industry whose tools played an unexpected role in the sophisticated attack.
Binance announced that it is currently working to establish a dedicated security research fund alongside developing targeted collaborative initiatives with leading AI companies, prominent blockchain industry participants, and specialized cybersecurity firms. This proposed collaboration will focus heavily on strengthening AI security standards within complex blockchain environments, though the exchange has not yet publicly disclosed the proposed financial size of the fund, the specific participating companies, or an official launch date.
As part of its immediate corporate response, the exchange plans to significantly expand its capital spending on advanced AI-enabled threat detection, comprehensive endpoint protection, developer-environment security hardening, and real-time behavioral anomaly monitoring.
Binance confirmed that it has already completely rebuilt the affected internal AI tool and underlying wallet infrastructure, replaced all compromised employee hardware devices, and substantially tightened internal access controls across the board. To ensure maximum transparency and technical rigor, Binance has also commissioned an independent cybersecurity review to thoroughly validate its internal investigation and identify any additional defensive safeguards required.
The company reported that approximately $2.85 billion of the total $6.34 billion in affected digital assets has been successfully frozen or intercepted, while 98% of the impacted token assets had been fully replenished out of corporate reserves as of Oct. 31.
However, the ongoing independent review has yet to establish the full, definitive extent of the underlying systemic weaknesses that initially allowed attackers to infiltrate and exploit the exchange’s internal AI environment. The final findings of this review are expected to directly inform the structural security changes Binance plans to implement as it formalizes its proposed industry-wide defense fund.