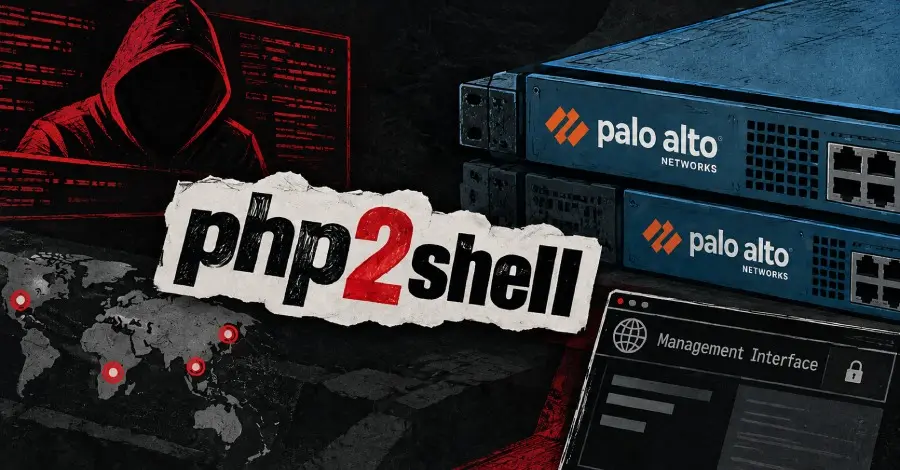
Palo Alto Networks has issued an urgent security warning, confirming that threat actors are actively exploiting recently patched vulnerabilities known as "PHP2Shell" against publicly accessible management interfaces. The disclosure follows a series of escalating security alerts regarding the critical flaws, which have already drawn the attention of cybersecurity researchers and government agencies worldwide.
The network security company stated in an update to its advisory that active exploitation has been observed targeting management interfaces exposed directly to the internet. The vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619, carry a severe CVSS score of 9.2. Together, these security flaws allow unauthenticated remote code execution on systems running vulnerable versions of PHP.
The underlying issues were originally addressed upstream by the PHP Foundation on October 21, 2026, with patches released for versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35. However, the window between the upstream patch release and widespread deployment across enterprise environments has provided malicious actors with an opportunity to mount automated and targeted attacks.

This latest development arrives just days after Israeli cybersecurity firm Dream reported observing a suspected China-nexus threat actor weaponizing the flaws. According to Dream’s findings, attackers chained the PHP2Shell vulnerabilities with a local privilege escalation bug in the Linux kernel, tracked as Fragnesia under the identifier CVE-2026-46300 with a CVSS score of 7.8. This dangerous combination was reportedly used to root 25 servers deployed across the United States, Japan, Taiwan, and South Korea. Among the compromised targets were three systems belonging to a U.S. government-affiliated environment, highlighting the elevated risk level associated with these exploits.
Dream noted that the affected devices were running specific versions of a large vendor’s firewall software. Following initial access and privilege escalation, the attackers reportedly launched subsequent campaigns directed at Active Directory environments. Recovered digital artifacts from the incidents confirmed that the malicious actors engaged in credential extraction and directory enumeration, laying the groundwork for deeper network penetration.
Although Dream did not explicitly name the affected firewall vendor in its initial disclosure, the timing of Palo Alto Networks’ updated advisory strongly suggests a correlation. Furthermore, while other major network security vendors have not yet reported widespread malicious exploitation against their respective product lines, the convergence of intelligence reports has elevated industry-wide vigilance.
In response to the escalating threat landscape, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-46300 to its Known Exploited Vulnerabilities catalog. The federal directive mandates that civilian government agencies apply required fixes by October 31, 2026. CISA emphasized in its advisory that this particular vulnerability can be seamlessly chained with CVE-2026-109618 and CVE-2026-109619 to successfully implant PHP web shells and execute arbitrary commands with root privileges.

Palo Alto Networks has clarified that no specialized configuration is required for systems to be vulnerable, noting that the risk level spikes dramatically on PAN-OS deployments where access to the management interface is permitted from external IP addresses on the public internet. The company reiterated that the issue strictly impacts the management web interface, which encompasses both the HTTPS web user interface and the XML API service. Dataplane interfaces are only affected if an administrative management profile is explicitly attached to them.
Palo Alto Networks has underscored that the security risks posed to PAN-OS and Panorama environments can be substantially mitigated by restricting access to the management interface exclusively to trusted internal IP addresses, in strict accordance with the vendor’s recommended best practice deployment guidelines. Additionally, customers utilizing Frontier Virtual Patching through ATP Plus on PAN-OS versions 12.2.4 and later have received advance coverage delivered via Threat ID 543004, which was deployed globally.
As organizations scramble to audit their external perimeters and apply upstream PHP patches alongside vendor-specific updates, cybersecurity authorities continue to urge immediate remediation. With nation-state-linked actors actively weaponizing the PHP2Shell and Fragnesia vulnerability chain, maintaining internet exposure on critical network management infrastructure remains one of the most hazardous security postures an enterprise can maintain.