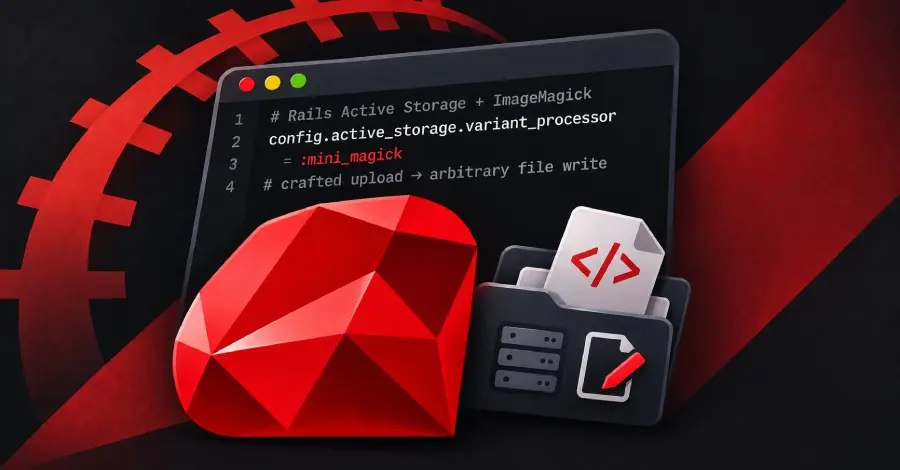
A severe and critical security flaw has been discovered within Ruby on Rails, one of the world’s most popular web application frameworks. The vulnerability, which carries a maximum CVSS severity score of 9.8 out of 10, presents a significant risk to applications that handle file uploads using ImageMagick. If exploited, an unauthenticated remote attacker could leverage a specially crafted file upload to write arbitrary files onto an application’s underlying server. Furthermore, depending on the server architecture and storage configuration, the vulnerability could also allow malicious actors to read sensitive system files, potentially paving the way for remote code execution and lateral movement across interconnected enterprise systems.
The core of the vulnerability resides within Active Storage, the built-in subsystem responsible for managing file uploads in Ruby on Rails applications. While Active Storage supports various storage backends, many applications rely on its native Disk service to store uploaded files directly on the server’s local disk storage. In environments configured this way, the security implications are profound. An attacker capable of exploiting the file-writing capability could theoretically read any file that the application process itself has permissions to access. According to advisories released by the Rails core team, these readable assets frequently include critical internal configuration artifacts such as the application’s secret_key_base and authentication credentials for third-party systems, databases, and microservices.
The security defect has been formally tracked under the identifier GHSA-f3w6-w445-fwh9. Although a Common Vulnerabilities and Exposures (CVE) identifier has not yet been assigned at the time of disclosure, the severity of the issue prompted immediate and decisive action from the Rails development team. The vulnerability was officially disclosed through a comprehensive GitHub security advisory and patched in newly released framework versions 8.1.4.1 and 8.0.5.2.
The mechanics of the vulnerability involve how ImageMagick processes incoming graphical data and interacts with specialized format handlers, which the library refers to as coders. ImageMagick dynamically selects an appropriate coder based on the intrinsic content of a file rather than its outer extension or declared MIME type. Certain specialized coders are designed to operate not on the pixel data of an image itself, but rather on other external files explicitly referenced within the interior structure of the uploaded file. Because Active Storage previously imposed no strict validation or limitations on which coders an incoming upload was permitted to invoke, the security boundaries of the server relied entirely on the host environment’s default ImageMagick security policy, which often proved insufficient.
Crucially, the vulnerability is triggered the exact moment a file is attached within the system. The Rails security advisory clarifies that the exploit path can be reached simply by attaching the malicious upload to a record. The application is not required to generate a visual variant—such as a resized or transformed copy of the image—nor does it need to invoke a preview generation routine or explicitly call an analysis method for the flaw to manifest.

Detailed analysis of the official commit used to remediate the vulnerability reveals that an attacker could upload a maliciously crafted Scalable Vector Graphics (SVG) file that successfully targeted ImageMagick’s MSL coder through the Active Storage analyzer. MSL, which stands for Magick Scripting Language, is a powerful scripting coder capable of reading and writing arbitrary files specified within the parameters of its internal script commands.
The vulnerability was responsibly identified and reported to the Ruby on Rails security team through the HackerOne bug bounty platform by security researcher RyotaK, a specialist working with GMO Flatt Security. While the Rails core team confirmed that at least one fully functional attack chain was demonstrated and reported to them during the disclosure process, they have emphasized that they do not assume it is the sole vector existing in the wild. At the time of publication, the advisory did not specify whether the vulnerability has been actively exploited in real-world cyberattacks against production environments.
Determining Affected Applications and Associated Flaws
For a Ruby on Rails application to be considered vulnerable to this critical flaw, a specific set of operational conditions must be met simultaneously. Security analysts and system administrators reviewing their codebases must check whether their application processes file uploads using ImageMagick as the underlying processor, which is determined by evaluating the config.active_storage.variant_processor configuration setting. If this configuration is left explicitly unexpressed, the framework falls back on default behaviors dictated by the application’s load_defaults framework target: applications utilizing configurations prior to version 7.0 defaulted to :mini_magick, whereas versions 7.0 and later default to :vips. Notably, this exact configuration setting governs which underlying library is invoked to analyze file attachments, extending its scope far beyond simple image transformations.
All Active Storage framework versions released prior to version 8.0.5.2 are impacted by the vulnerability, alongside versions within the 8.1 release series predating version 8.1.4.1. Framework release series older than version 8.0 have reached their official end-of-life and are no longer supported by the maintenance team, meaning official security backports will not be provided for legacy installations. Organizations running older, unsupported versions must either upgrade their entire framework stack or implement strict manual mitigations at the operating system and library levels.
The release of these patches coincides with the disclosure of a separate high-severity Active Storage vulnerability tracked as GHSA-v924-7rp8-4mxh, which has been assigned a CVSS score of 8.8. In this secondary vulnerability, Active Storage passed user-supplied uploads to ImageMagick and FFmpeg utilizing temporary file names that preserved the original file extension provided during the upload process. Consequently, these multimedia processing utilities could fall back on selecting a decoder based purely on the file extension when the internal file content was ambiguous or lacked clear formatting signatures. This design choice allowed a malicious actor who controlled both the upload filename and the declared content type to manipulate the system into selecting a specific, potentially unsafe decoder.
These newly issued patches arrive only months after Rails addressed another critical Active Storage vulnerability in July, designated as CVE-2026-66066. That previous security defect impacted applications configured to utilize the libvips library instead of ImageMagick. While applications running ImageMagick were safely insulated from the specific attack path of the July vulnerability, the newly disclosed flaws demonstrate that ImageMagick-backed installations carry their own distinct and severe attack surfaces.

Recommended Remediation Steps
Given the severity of the vulnerabilities, the Ruby on Rails core team strongly advises all maintainers and system administrators to upgrade their applications immediately. The newly deployed maintenance releases address a total of 21 distinct security issues across the framework and its associated components, reinforcing the necessity of a prompt system-wide update.
As part of the remediation effort, the newly released framework versions incorporate a robust, restrictive ImageMagick security policy by default. MiniMagick, the standard Ruby gem utilized by Active Storage to interface with the underlying ImageMagick binaries, enforces this security policy across every command it executes, ensuring that security boundaries are maintained not just for Active Storage operations, but for all application-level image processing tasks.
The integrated security policy explicitly blocks the execution of the MSL coder, alongside any other coders designed to read, write, or delete files external to the primary image asset. Furthermore, the policy disables coders capable of fetching remote or local network references, rendering them to a display device, and strips out support for every coder backed by Ghostscript, as well as the associated gs delegate and @filename indirection mechanisms.
Because the newly released security advisories do not provide specific forensic guidelines or indicators of compromise to determine whether an application has already been targeted or compromised prior to patching, organizations are encouraged to review their server access logs, inspect temporary storage directories for unauthorized file modifications, and audit user upload directories for anomalous activity. Security teams should prioritize patching their dependencies and verifying that their deployment pipelines successfully incorporate the updated framework versions to safeguard against potential exploitation.