As market charts flip from red to green, the cryptocurrency lending sector is experiencing a significant resurgence of interest following a particularly dismal second quarter that left many market participants cautious about the stability of decentralized finance ecosystems.
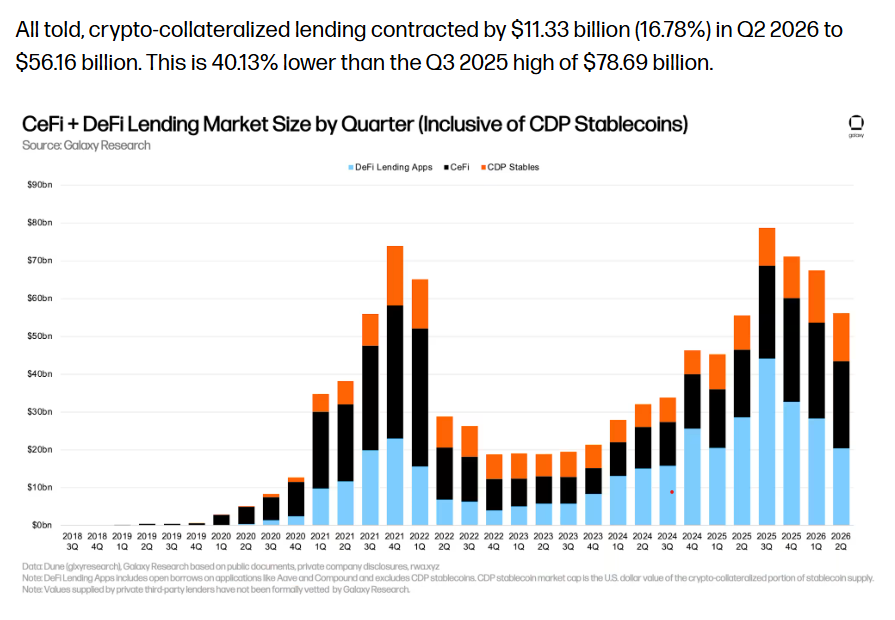
Figures compiled by Galaxy show that $11.33 billion left the sector during Q2. This massive capital flight was driven in part by a severe crisis of confidence among lenders, triggered by the Kelp DAO hack in April. That exploit left users of Aave—widely regarded as one of the most trusted protocols in the decentralized finance space—temporarily unable to access their Ether.
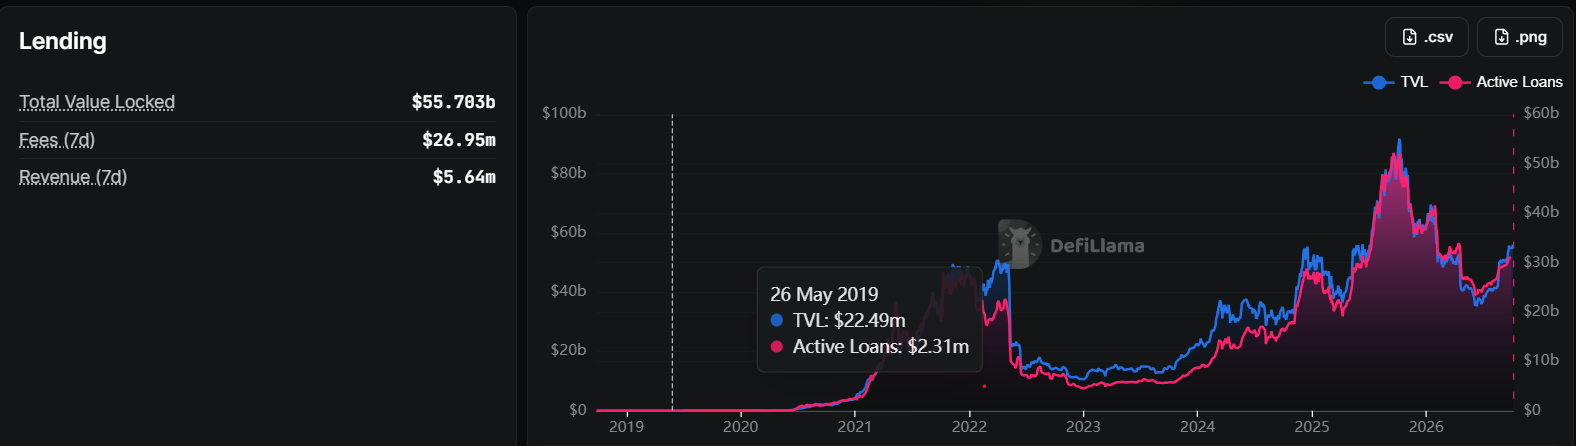
However, since the beginning of July, the total value locked (TVL) in crypto lending has rebounded dramatically, gaining more than 55% to sit comfortably around $56 billion today.
While this rapid influx of capital signals renewed market confidence, it also means the financial honeypot has grown substantially larger. This dynamic raises a critical question for the industry: Can users truly trust interlinked DeFi lending protocols in an era of AI-assisted hacks, where a single exploit in one isolated protocol can trigger a cascade of devastating effects across every connected platform?
Stani Kulechov, founder and chief executive of Aave Labs, notes that this systemic vulnerability is now top of mind for developers and risk managers across the entire ecosystem.
“When a protocol accepts a token as collateral, it is also accepting that token’s bridge, its verifier configuration, its oracle and its issuer’s operational security,” Kulechov explains.
That exact interconnected reality is what ultimately landed Aave in the middle of a major liquidity scare earlier in the year.
An Expanding Attack Surface
When malicious actors exploited a Kelp DAO cross-chain route back in April, they successfully manufactured 116,500 unbacked rsETH tokens, which were valued at approximately $290 million at the time of the breach. A significant portion of these fraudulently minted tokens was subsequently posted as collateral to borrow other valuable assets across various Aave markets.
Even though Aave’s own native smart contracts were not directly breached or compromised during the incident, the protocol still suffered immense collateral damage. Deposits plummeted by roughly $15 billion in the immediate aftermath of the exploit, forcing the platform to take emergency action by freezing its rsETH and wrsETH lending and borrowing markets to contain the contagion.
Kulechov explains that the harrowing experience prompted Aave to completely overhaul its security philosophy, shifting toward a much more holistic risk-management framework.
“We rebuilt our approach around that wider view,” he says, emphasizing that security protocols can no longer afford to stop at the smart contract level. He adds that traditional security reviews historically “missed the risk sitting in the bridges, verifier networks and other infrastructure an asset depends on.”
As the broader market recovers, regular users of decentralized lending protocols will similarly need to exercise caution when judging how heavily exposed a specific platform is to both internal and external risks.
“Every wrapper, bridge and oracle between the lender and the underlying asset is another place a loan can go wrong,” points out Thomas Wu, chief financial officer of Bitcoin-backed lender Ledn.
Sid Powell, co-founder and chief executive of crypto credit platform Maple, echoes this sentiment, arguing that serious lenders should always operate under the assumption that a borrower can fail at any given moment and work backward from that pessimistic baseline.
“What am I holding, where is it, can I see it in real time, and how quickly can I get to it if something breaks?” Powell asks, summarizing the core operational questions every credit manager should be asking.
When Security Fails, Containment Matters
Addressing systemic risk requires looking far beyond standard smart contract audits. Sam MacPherson, chief executive of rival DeFi lender Spark, explains that his team conducts thorough reviews of governance design, operational security, collateral quality, liquidity management, and dependencies running across the wider blockchain ecosystem.
Demonstrating its commitment to risk mitigation, Spark actually began phasing out rsETH support on SparkLend as early as January—months before the April Kelp exploit occurred. The decision was made after internal assessments concluded that the token’s low usage and revenue generation simply did not justify the additional systemic risk created by supporting it.
Kulechov notes that Aave has introduced similar proactive mechanisms, implementing a policy where every listed asset is re-reviewed on a quarterly basis and evaluated again immediately following any material operational change. According to Kulechov, the protocol has already initiated an orderly wind-down process across six different blockchain networks that ultimately failed to meet its upgraded chain-level standards.
“No protocol can control the entire ecosystem, but it can control how much of that risk it takes on and how quickly it responds,” Kulechov states.
While preventing structural failures remains the ultimate ideal, protocols must also maintain clear, actionable procedures to respond swiftly if the worst-case scenario occurs, MacPherson argues.
“Preventing losses is only part of the challenge,” MacPherson notes. “Protocols also need to demonstrate how a loss would be contained if something does go wrong.”
The Margin for Human Error
Technical vulnerabilities in code are only part of the equation. Shawn Owen, founder and chief executive of SALT Lending, points out that human error remains one of the single greatest vulnerabilities in the entire financial ecosystem—and ironically, it is often the easiest factor for protocols and users alike to overlook.
“A lot of the biggest losses have come down to key management, access controls or someone getting socially engineered, and a smart contract audit won’t catch any of that,” Owen explains.
Additional layers of risk materialize when customer assets are deployed elsewhere in the market to generate supplementary interest. Crypto lenders learned that bitter lesson during the brutal market unwind of 2022, when centralized platforms such as Celsius, Voyager, and BlockFi completely imploded after taking on speculative risks that their customers either did not understand or never expected them to take.
To minimize its overall attack surface, Ledn takes a conservative approach by storing client Bitcoin with qualified institutional custodians rather than aggressively lending it out to chase additional yield.
Wu explains that every single external transaction introduces an additional point of failure where something can potentially go wrong, meaning that reducing transactional touchpoints naturally lowers the overall risk of a catastrophic security breach.
“The only way to take those risks off the table is to keep client Bitcoin in segregated custody, with tight controls and as few movements as possible,” Wu says.
Powell warns that during periods when customer deposits begin flowing into a platform faster than managers can find viable, high-quality places to deploy them, mounting pressure to maintain attractive yields can easily lead to poor decision-making.
“So they take on a little more risk to get there. Maybe the collateral standards get looser, or they lend to a borrower they’d have turned down a year ago,” Powell explains. “The managers who hold up in a downturn are usually the ones who were willing to say no to capital when they didn’t have a good place to put it.”
Can AI Make Lending Safer?
Amid ongoing headlines regarding sophisticated AI-driven hacks, malicious exploits, and autonomous software agents occasionally escaping human control, artificial intelligence may ironically hold the key to making crypto lending significantly safer.
Aave is already actively utilizing AI-assisted testing alongside its conventional security procedures. The platform recently employed mutation testing to deliberately and artificially introduce bugs into its upcoming V4 smart contracts, finding that its automated test suites successfully caught 271 out of 304 injected vulnerabilities.
In a comprehensive security review covering both its V3 and V4 codebases, three distinct AI security tools generated a combined 71 findings. After thorough manual reviews by human engineers, 20 of those findings were validated as genuine security concerns. The remaining 51 false positives clearly demonstrated why human security experts and auditors will likely remain gainfully employed for the foreseeable future.
“AI is very good at breadth and speed,” Kulechov observes, “but around 70% of the raw findings were false positives, so expert judgment stays essential.”
At the same time, artificial intelligence remains a delicate double-edged sword. As AI agents increasingly take on the responsibility of managing capital directly on-chain, their specific permissions, operational inputs, and underlying decision-making logic transform into critical new attack surfaces that require robust security as much as any traditional smart contract.
As the crypto lending industry resumes its upward trajectory, the core challenge facing developers and institutional participants alike is no longer just keeping basic code secure. It requires ensuring that every interconnected piece of the modern decentralized finance puzzle is thoroughly understood, continuously monitored, and reliably contained when unexpected failures occur.