As the broader cryptocurrency market charts flip from red to green, the crypto lending sector has experienced a remarkable resurgence of interest following a particularly dismal second quarter. The market’s dramatic contraction earlier in the year left many industry participants questioning the resilience of decentralized finance (DeFi), but capital has rapidly returned as sentiment has shifted.
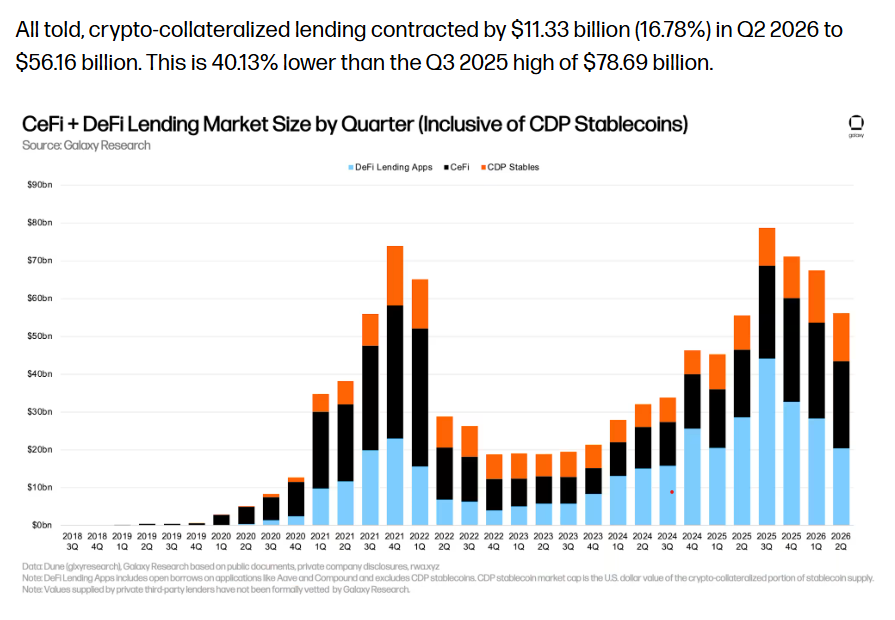
According to data compiled by analytics firm Galaxy, an estimated $11.33 billion left the crypto lending sector during the second quarter. This massive capital flight was driven in part by a severe crisis of confidence among users and lenders alike. The panic was largely catalyzed by the Kelp DAO hack in April, an exploit that abruptly left users of Aave—widely regarded as one of the most trusted and robust protocols in the decentralized finance ecosystem—temporarily unable to access their Ethereum holdings.
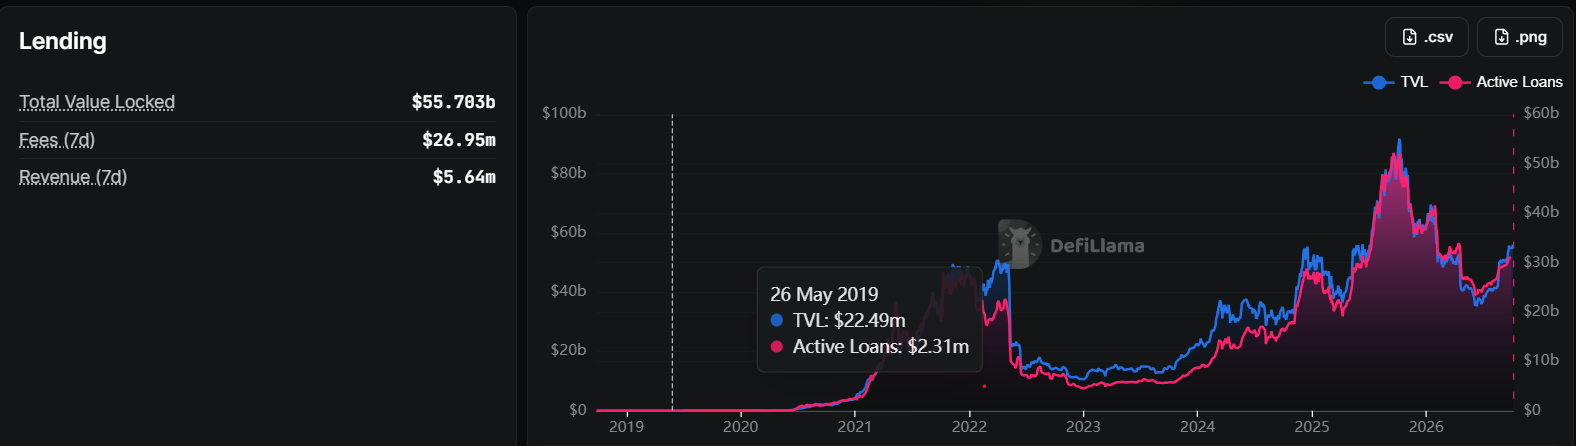
However, the tide has turned dramatically since the beginning of July. Total lending value locked across the sector has gained more than 55%, climbing from its quarterly lows to sit comfortably around $56 billion today, according to data from DeFiLlama.
This swift recovery, however, means the financial honeypot has grown significantly larger once again. It also revives a critical, underlying question for the entire ecosystem: Can users truly trust interlinked DeFi lending protocols in the era of sophisticated, AI-assisted hacks? In today’s highly composable financial landscape, an exploit targeting any single protocol can trigger a cascading series of devastating effects for other protocols connected to it through shared assets, bridges, and oracles.
Stani Kulechov, founder and chief executive of Aave Labs, notes that this systemic interconnectivity is now a top-of-mind priority for protocol architects and developers across the industry.
"When a protocol accepts a token as collateral, it is also accepting that token’s bridge, its verifier configuration, its oracle and its issuer’s operational security," Kulechov explains.
That complex web of dependencies is precisely what landed Aave in trouble earlier this year, exposing the vulnerabilities inherent in modern multi-chain crypto markets.
An Expanding Attack Surface
The structural vulnerabilities of composable finance were laid bare in April when malicious actors successfully exploited a Kelp DAO cross-chain route. During the incident, the attackers minted 116,500 unbacked rsETH tokens, which were valued at approximately $290 million at the time. A significant portion of those illicitly generated tokens were subsequently posted as collateral across various markets to borrow other high-value assets on Aave.
Even though Aave’s own native smart contracts were not directly breached during the attack, the protocol suffered immediate collateral damage. Deposits across the platform plummeted by around $15 billion in the days immediately following the exploit. To protect its user base and prevent further systemic risk, Aave was forced to swiftly freeze its rsETH and wrsETH borrowing markets.
Reflecting on the incident, Kulechov emphasizes that Aave has since shifted toward a much broader, more comprehensive approach to platform security.
"We rebuilt our approach around that wider view," Kulechov says, noting that the protocol’s fundamental starting point is that security can no longer stop at the smart contract level. He adds that traditional security audits and code reviews historically "missed the risk sitting in the bridges, verifier networks and other infrastructure an asset depends on."
As the market continues to expand, users of lending protocols will similarly need to evaluate how deeply exposed any given protocol is to both external and internal risks.
"Every wrapper, bridge and oracle between the lender and the underlying asset is another place a loan can go wrong," points out Thomas Wu, chief financial officer of Bitcoin-backed lender Ledn.
Similarly, Sid Powell, co-founder and chief executive of crypto credit platform Maple, stresses that serious lenders should operate under the assumption that a borrower or underlying asset can fail at any given moment, working backward from that worst-case scenario.
"What am I holding, where is it, can I see it in real time, and how quickly can I get to it if something breaks?" Powell asks, outlining the rigorous mental framework required for sustainable lending operations.
When Security Fails, Containment Matters
Addressing these multifaceted vulnerabilities requires looking far beyond standard smart contract audits. Sam MacPherson, chief executive of DeFi lender Spark, explains that his team reviews a wide array of factors, including governance design, operational security, collateral quality, liquidity management, and complex dependencies across the broader blockchain ecosystem.
Spark’s proactive risk management was evident earlier in the year when the platform began phasing out rsETH on SparkLend in January—months before the April Kelp exploit occurred. The decision was made after internal assessments concluded that the asset’s low usage and minimal revenue did not justify the additional risk introduced by supporting it.
Kulechov notes that Aave has introduced remarkably similar governance and risk-mitigation mechanisms. Under the updated framework, every listed asset is subjected to rigorous quarterly re-reviews, as well as mandatory evaluations immediately following any material change to the asset’s infrastructure. Kulechov reveals that the protocol has already initiated an orderly wind-down process across six different networks that failed to meet its heightened chain-level standards.
"No protocol can control the entire ecosystem, but it can control how much of that risk it takes on and how quickly it responds," Kulechov states.
While preventing failures remains the primary objective, protocols must also maintain clear, actionable procedures to contain the damage if an unforeseen incident does occur, according to MacPherson.
"Preventing losses is only part of the challenge," MacPherson notes. "Protocols also need to demonstrate how a loss would be contained if something does go wrong."
The Margin for Human Error
Beyond technical exploits and faulty cross-chain bridges, human error remains one of the single greatest vulnerabilities in the crypto lending space—and arguably the easiest one to overlook in the shadow of complex smart contract code.
Shawn Owen, founder and chief executive of SALT Lending, points out that operational vulnerabilities frequently stem from simple administrative oversights rather than flawed code logic.
"A lot of the biggest losses have come down to key management, access controls or someone getting socially engineered, and a smart contract audit won’t catch any of that," Owen explains.
Additional risks invariably materialize when centralized or decentralized lenders deploy customer assets elsewhere in pursuit of yield generation. The crypto lending industry learned this hard lesson during the brutal market unwind of 2022, when major lenders such as Celsius, Voyager, and BlockFi spectacularly imploded after taking on speculative risks that their customers either did not fully understand or never agreed to take.
To minimize its overall attack surface and protect user funds, Ledn deliberately avoids the temptation to deploy client Bitcoin into external yield-generating strategies. Instead, the firm keeps client assets securely stored with qualified custodians.
Wu emphasizes that every transaction represents an additional point of potential failure, meaning that simplicity directly correlates with safety.
"The only way to take those risks off the table is to keep client Bitcoin in segregated custody, with tight controls and as few movements as possible," Wu asserts.
Powell offers a similar cautionary note regarding market dynamics, warning that when capital inflows outpace a manager’s ability to identify legitimate, high-quality lending opportunities, the intense pressure to maintain attractive yields frequently drives poor decision-making.
"So they take on a little more risk to get there. Maybe the collateral standards get looser, or they lend to a borrower they’d have turned down a year ago," Powell explains. "The managers who hold up in a downturn are usually the ones who were willing to say no to capital when they didn’t have a good place to put it."
Can AI Make Lending Safer?
Even as the industry grapples with headlines regarding AI-assisted hacks, sophisticated cyber exploits, and autonomous software agents occasionally escaping human control, artificial intelligence may paradoxically serve as a powerful tool to make crypto lending significantly safer.
Aave, for instance, has already integrated AI-assisted testing alongside its conventional security procedures. In recent trials, the protocol utilized mutation testing to deliberately inject hundreds of artificial bugs into its V4 smart contracts. Impressively, its automated AI-driven test suites successfully caught 271 out of 304 injected vulnerabilities.
In a comprehensive security review of its V3 and V4 codebases, three separate AI security tools generated a combined 71 findings. After thorough manual reviews by human security researchers, 20 of those findings were validated as genuine security concerns. The remaining 51 false positives highlighted precisely why human security experts and auditors will likely remain indispensable to the industry for the foreseeable future.
"AI is very good at breadth and speed," Kulechov observes, "but around 70% of the raw findings were false positives, so expert judgment stays essential."
At the same time, artificial intelligence represents a distinct double-edged sword for the sector. As AI agents increasingly assume autonomous roles in managing on-chain capital, their permissions, data inputs, and underlying decision logic inevitably transform into a new and complex attack surface that requires rigorous protection.
"As AI agents start managing capital on-chain, their permissions, inputs and decision logic become things that need to be secured just like a contract," Kulechov concludes.
As the crypto lending ecosystem rebounds toward previous heights, the fundamental challenge facing developers and institutional participants alike is no longer merely writing secure code. Rather, it is ensuring that every interconnected piece of the modern decentralized financial puzzle is thoroughly understood, continuously monitored, and reliably contained the moment something unexpected goes wrong.