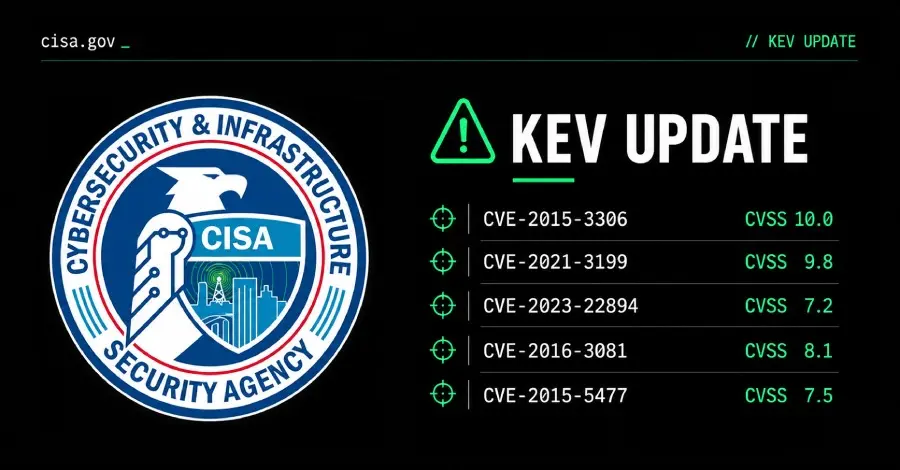
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five critical security flaws to its Known Exploited Vulnerabilities (KEV) catalog following widespread abuse by a China-linked threat actor known in the cybersecurity community as Flax Typhoon. The move comes as part of a coordinated international effort to counter sophisticated cyber espionage campaigns targeting critical infrastructure, corporate networks, and government systems across the globe.
The addition of these five vulnerabilities coincides with the release of a sweeping joint advisory issued by cybersecurity authorities from Australia, Canada, Japan, New Zealand, Spain, the United Kingdom, and the United States. This international warning highlights malicious cyber operations enabled by a China-based cybersecurity company identified as Integrity Technology Group. According to intelligence shared by Western agencies, these state-backed operations utilize front companies and commercial enterprises to mask extensive cyber espionage campaigns and unauthorized network intrusions.
Investigative findings reveal that these threat actors systematically target a total of eight security vulnerabilities—including the five newly cataloged flaws and three others previously added to the KEV repository—to obtain initial access to victim networks and siphon sensitive data. The multi-stage attack lifecycle typically involves the deployment of automated scanning tools to discover vulnerable systems, cross-site scripting (XSS) attacks, and aggressive password-spraying techniques directed at Microsoft Exchange servers. Once initial access is achieved, the threat actors establish persistence using compromised virtual private network (VPN) software and deploy custom scripts to covertly exfiltrate valuable internal emails, corporate documents, and user credentials.

The discovery underscores a persistent and alarming trend highlighted by federal officials regarding foreign adversaries infiltrating foundational operational networks. "Chinese government-affiliated actors continue to position themselves within critical infrastructure networks, including operational technology (OT) systems, with the aim of disrupting critical functions at a future time of their choosing," said Acting Executive Assistant Director for Cybersecurity Chris Butera. These pre-positioning activities are designed to grant foreign intelligence agencies deep access and leverage over vital services, ranging from energy and water management to transportation and communications networks, should geopolitical tensions escalate.
The timing of the KEV catalog updates follows significant disruption operations led by law enforcement and intelligence agencies. Recently, coordinated law enforcement actions, including operations by the Federal Bureau of Investigation (FBI), successfully seized multiple domains and disrupted the operational infrastructure of Flax Typhoon, severely hampering their ability to maintain command and control over compromised devices. However, despite these operational setbacks, the underlying vulnerabilities exploited by the group remain a severe and active risk to organizations that have not yet applied the necessary software patches.
In response to the active exploitation documented in the joint international advisory, federal civilian executive branch agencies in the United States are now under strict directives to remediate the risks. Agencies are required to apply all necessary software patches or completely discontinue the use of the affected products by October 11, 2026. While the mandate specifically targets federal departments, CISA strongly urges private sector organizations, critical infrastructure operators, and enterprise IT administrators to treat the KEV catalog updates with the highest level of urgency and to review their network perimeters for signs of compromise associated with Flax Typhoon and Integrity Technology Group.