
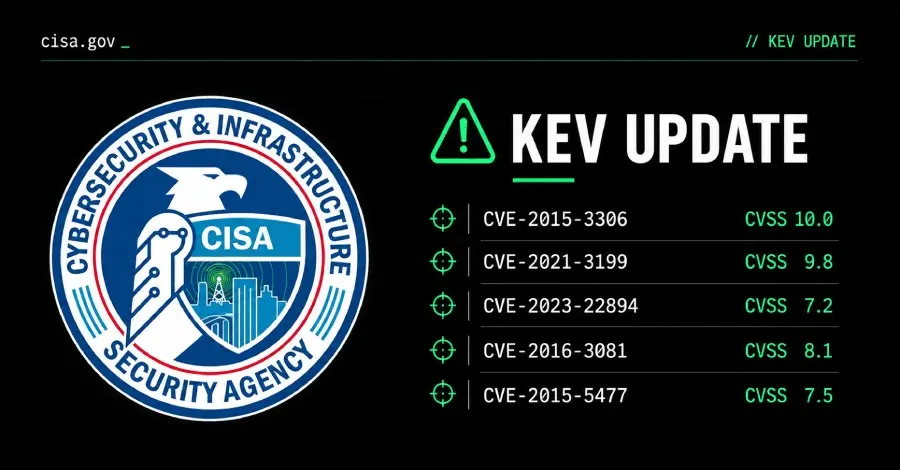
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, following their active abuse […]
Tag: five
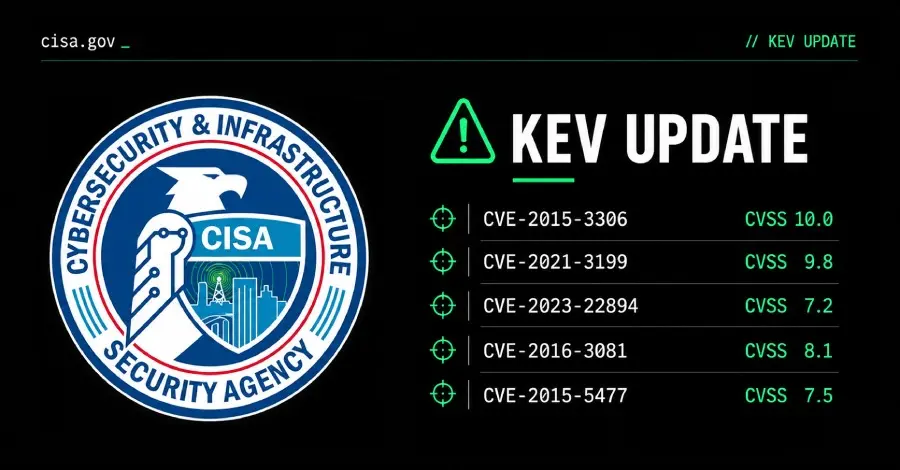
CISA Adds Five Flaws to KEV Catalog Following Exploitation by China-Linked Flax Typhoon and Integrity Technology Group
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five critical security flaws to its Known Exploited Vulnerabilities (KEV) catalog following widespread abuse by […]
Five-Year Analysis of Proofpoint’s Voice of the CISO Reports Reveals Shift in Enterprise Risk from Perimeters to Workflow
The enterprise cybersecurity landscape is undergoing a profound transformation, moving away from a predictable line of escalation toward a complex convergence of human behavior, artificial […]