A newly identified China-nexus cyber espionage group, designated as TA419, has emerged as a significant threat to the artificial intelligence sector, orchestrating a series of sophisticated credential phishing campaigns directed at AI policy experts, researchers, and professionals. According to recent threat intelligence reports, these malicious operations have specifically targeted individuals working within prominent U.S. think tanks, major universities, and critical legal sector organizations, marking an evolution in Beijing-aligned cyber intelligence collection priorities.
Security researchers tracking the group indicate that these campaigns leverage highly tailored social engineering tactics, frequently impersonating high-profile economists, prominent artificial intelligence policymakers, and even key industry employees. By establishing a veneer of credibility through targeted outreach, TA419 seeks to harvest enterprise credentials and compromise sensitive accounts across organizations operating at the intersection of technology and public policy.
The activity is viewed by cybersecurity analysts as a direct reflection of broader geopolitical and strategic competition between the United States and China. As governments grapple with complex regulatory frameworks, export controls on advanced semiconductors, and contentious debates surrounding model distillation and national security, foreign intelligence services have increasingly turned their attention toward policy architects and technical specialists who shape the future of artificial intelligence governance.
Evolution of the TA419 Threat Actor
While the designation TA419 is relatively new, the underlying adversary has a documented history of espionage-motivated cyber activity. Enterprise security firm Proofpoint, which detailed the group’s operations in an extensive analysis published this week, notes that the threat actor has actively orchestrated credential phishing campaigns against individuals associated with U.S. and Japanese think tanks, defense contractors, academic institutions, and law firms since at least April 2025.

Historically, TA419’s operational remit has centered heavily on defense, national security, energy, international relations, and foreign policy targets, predominantly focusing on entities with a clear U.S. and Japanese nexus. The recent pivot toward artificial intelligence policy experts does not represent a departure from these traditional intelligence priorities, but rather an extension of them. As artificial intelligence becomes inextricably linked to national security and economic competitiveness, intelligence collectors are naturally shifting resources to monitor developments in this critical domain.
Documented instances of the group’s methodology highlight a high degree of patience and preparation. For example, in February 2026, threat actors singled out a prominent artificial intelligence policy expert at a major U.S. think tank. The attackers utilized a carefully crafted persona, impersonating a well-known employee of the AI company Anthropic, and deployed a phishing email bearing the subject line "Request for Feedback on Military Integration of Claude."
Subsequent campaigns observed around July 2026 demonstrated a similar level of operational sophistication. During this wave, TA419 operators impersonated several notable figures, including a former member of the leadership team within the White House Office of Science and Technology Policy, reinforcing their focus on individuals who influence the federal regulatory landscape.
Multi-Stage Delivery and Advanced Evasion Techniques
The anatomy of a TA419 attack typically begins with low-friction, seemingly innocuous outreach designed primarily to establish rapport and trigger a response from the target. Rather than immediately launching malicious payloads or suspicious links, the adversary initiates contact with harmless invitations or professional inquiries. It is only after the recipient responds that the second phase of the operation is set into motion.
Upon receiving a reply from the target, the adversary follows up with a shortened URL. Clicking this link initiates a complex, multi-stage redirection chain. Before reaching the final destination, the traffic is routed through a Cloudflare Turnstile check, a mechanism ostensibly used to filter out automated security scanners and sandbox environments, thereby ensuring that only human targets using legitimate browsers reach the infrastructure.

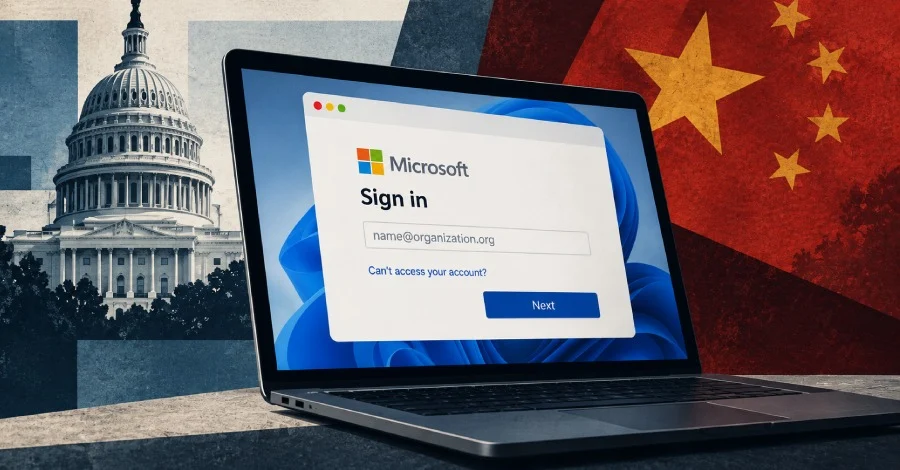
Once past the verification check, the victim is directed to a Microsoft OneDrive-themed adversary-in-the-middle (AitM) credential phishing page. To maximize the illusion of authenticity, TA419 employs a sophisticated attack methodology known as Frameless BitB, which builds upon traditional browser-in-the-browser techniques.
Traditional BitB attacks simulate a trusted website or login prompt by rendering a fake browser window within an iframe inside a legitimate browser session using standard web technologies like HTML, CSS, and JavaScript. In contrast, Frameless BitB achieves the exact same visual deception without relying on the iframe element. Security researchers, including Wael Masri who documented the technique, have explained that this is accomplished by injecting scripts and HTML directly into the original content via substitutions, subsequently relying entirely on advanced CSS and JavaScript styling to recreate the visual appearance of a native browser window and login prompt.
Custom Tooling and Session Hijacking
What sets TA419 apart from standard commodity phishing operations is the integration of custom-built tooling designed to subvert modern authentication controls. According to Proofpoint’s analysis, the threat actor has taken open-source frameworks and augmented them with a bespoke telemetry and automation module.
This custom module is engineered to monitor the victim’s Microsoft sign-in process in real time. As the user attempts to authenticate, the AitM proxy captures the entered credential information while simultaneously relaying the data to legitimate Microsoft infrastructure in the background. Because the proxy facilitates a real connection to the actual service, the authentication event succeeds from the victim’s perspective.
The primary advantage of this technique for the attacker is transparency. The victim notices nothing amiss, as the login completes successfully without generating standard error messages or warning signs. Crucially, the resulting session cookies—which grant ongoing access to the account—are stealthily captured by the adversary, allowing them to bypass traditional multi-factor authentication (MFA) protections without triggering additional prompts for the user.

Mitigating the Risk of Sophisticated Credential Theft
As state-sponsored groups continue to refine their social engineering and proxy-based attack vectors, cybersecurity experts emphasize that conventional security training alone is insufficient to protect high-profile individuals. Because TA419 utilizes highly convincing impersonations of real policy figures, government officials, and industry leaders, targets frequently lower their guard when reviewing seemingly professional correspondence.
To defend against advanced adversary-in-the-middle campaigns and frameless browser spoofing, organizations and high-risk individuals are strongly advised to adopt phishing-resistant authentication methods. Specifically, the implementation of hardware-backed passkeys or FIDO2-compliant security keys renders AitM and credential-harvesting proxies ineffective, as these protocols cryptographically bind the authentication session to the legitimate origin and cannot be easily relayed by an intermediary server.
Furthermore, security analysts recommend that professionals operating within sensitive fields—such as artificial intelligence policy, national security, foreign relations, and defense research—exercise heightened skepticism regarding unsolicited subject-matter outreach. Verifying the authenticity of communications through out-of-band channels before engaging or clicking on links remains a critical defense against targeted espionage campaigns.
As geopolitical competition continues to drive cyber espionage efforts toward emerging technological frontiers, intelligence groups like TA419 are expected to persist in their attempts to compromise the human element of the global policy ecosystem. Organizations must therefore maintain vigilance, continuously updating their defensive posture to counter the evolving sophistication of state-backed threat actors.