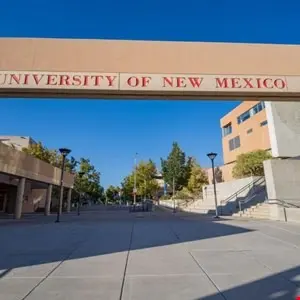
The University of New Mexico Health Sciences Center (UNM HSC) recently faced a severe operational disruption following a significant cybersecurity incident that forced the institution to halt medical services, cancel surgical procedures, and divert emergency ambulance traffic. The event, which sent shockwaves through the regional healthcare community, underscored the escalating vulnerability of major academic medical centers to sophisticated digital threats.
The crisis began on Monday, October 26, when UNM HSC leadership formally disclosed that the institution had been hit by a cyberattack. The announcement, released at approximately 2:30 p.m. Mountain Daylight Time, served as an urgent notification to patients, faculty, and staff. The immediate directive was clear: all scheduled appointments and surgeries for the remainder of the day were canceled.
In a statement issued to the public, the health center provided explicit instructions to the community: “UNM Health patients should not show up to UNM Health facilities on October 26. Emergencies should be handled by 911 and non-emergencies should be delayed until further notice.” This rapid suspension of services was a necessary precautionary measure to protect patient safety while IT security teams worked to assess the scope of the unauthorized network intrusion.
Clinical Services Resume Amidst Ongoing Academic Disruptions
The recovery phase commenced later that same evening. At 10:27 p.m. on October 26, UNM HSC officials provided a critical update, confirming that the health system’s hospitals had reopened. The administration indicated that clinical services, including regularly scheduled appointments and surgical procedures, were set to resume starting Tuesday, October 27.
“At 2:30 p.m., UNM Health began resuming operations and bringing systems back online in phases, as it was safe to do so,” the HSC statement noted. “We will work with patients to reschedule missed appointments and procedures.” While the clinical arm of the organization moved toward stabilization, the impact on the academic side remained pronounced.
The university took comprehensive steps to secure its digital environment by mandating that students enrolled in the School of Medicine, College of Pharmacy, College of Nursing, and College of Population Health vacate the campus. As part of its broader remediation strategy, UNM suspended classes on the Health Sciences campus and instructed non-essential personnel to return home.
The disruption extended into the following day. All classes at the affected colleges, including those conducted via online and remote platforms, were canceled for Tuesday, October 27. Non-essential staff were similarly directed to remain off-site to allow technical teams the space and bandwidth required to sanitize systems and restore core infrastructure. Notably, these disruptions were isolated to the Health Sciences sector; classes at UNM’s Central and branch campuses remained unaffected by the incident.
The Rise of the BYOD Ransomware Group
While the university initially provided limited details regarding the nature of the breach, the threat landscape quickly clarified as external cybersecurity entities began monitoring the situation. Reports emerged that a ransomware collective operating under the moniker "BYOD" had claimed responsibility for the attack.
The cybersecurity intelligence firm VenariX drew public attention to the incident by noting on the social media platform X that the BYOD group had listed the University of New Mexico on its dedicated data leak site. The group asserted that it had successfully compromised 36,000 machines across the university’s network, claiming to have exfiltrated a massive cache of sensitive data.
The attackers alleged that the stolen information included personally identifiable information (PII) belonging to students and employees, extensive research data, internal student records, and private institutional emails. On their leak site, the group issued a bold, aggressive statement, asserting, “This is your entire network and infrastructure compromised, the entire university COMPLETELY.”
This declaration highlights the increasingly aggressive tactics employed by modern ransomware gangs, who often seek to maximize leverage by exfiltrating vast amounts of sensitive information alongside encrypting network assets. For an institution of the scale of UNM HSC—which handles over one million patient visits annually, including approximately 900,000 outpatient appointments and 100,000 emergency room visits—the potential exposure of such data represents a significant privacy and regulatory concern.
Contextualizing the Vulnerability of Healthcare Infrastructure
The incident at UNM HSC is not an isolated event but rather a reflection of a broader, concerning trend in the healthcare sector. The digitization of patient records, the integration of complex medical devices into hospital networks, and the reliance on interconnected academic systems have transformed medical centers into prime targets for cybercriminals.
As healthcare facilities become more reliant on data-driven medicine, the consequences of a system outage become life-threatening. The diversion of ambulances, for instance, forces patients in critical condition to seek care at facilities that may be further away or less equipped to handle specific medical emergencies. This ripple effect places immense strain on regional emergency response systems and public health infrastructure.
The academic nature of the UNM Health Sciences Center adds another layer of complexity to the incident. Because the center is deeply intertwined with university research and education, the breach of its network potentially compromises years of intellectual property and sensitive academic findings. With a student body of 2,670 enrolled in its various health colleges as of 2025, the impact on the academic calendar and the privacy of these students is a significant burden for the institution to manage.
This attack follows a pattern observed globally, where the healthcare industry has seen a substantial increase in the frequency and severity of cyber-attacks. For example, similar reports have emerged from the UK, where the healthcare sector has faced a tenfold increase in cyber-attacks, highlighting the global scale of the threat. These incidents demonstrate that malicious actors are increasingly viewing healthcare providers as high-value targets, likely due to the high sensitivity of the data they hold and the urgent need for service continuity, which makes them more likely to consider ransom payments to minimize patient harm.
As the University of New Mexico moves forward, it faces the dual challenge of restoring full operational normalcy and navigating the long-term implications of a major data breach. The focus for administrators and IT security teams will likely remain on forensic analysis, system hardening, and communication with the affected parties whose information may have been compromised.
For the community served by UNM HSC, the incident serves as a stark reminder of the digital fragility inherent in modern healthcare. While clinics and hospitals have successfully brought their systems back online, the forensic investigation into how the BYOD group gained such deep access to the university’s infrastructure will likely continue for months. The university’s commitment to transparency in its communication—from the initial 2:30 p.m. disclosure to the phased restoration of services—has been central to managing the public response to the crisis. As they work to reschedule thousands of missed appointments and restore the academic experience for their students, the institution stands as the latest example of how quickly a digital threat can manifest as a real-world crisis in the heart of a major university health system.