Paolo Ardoino’s strategic push to integrate artificial intelligence into Bitcoin mining hinges on a fundamental operational and human decision: precisely who is authorized to grant a machine permission to alter its core behavior. As Tether’s open-source Mining Development Kit (MDK) gains traction across the digital asset ecosystem, the question of device autonomy versus human control has taken center stage.
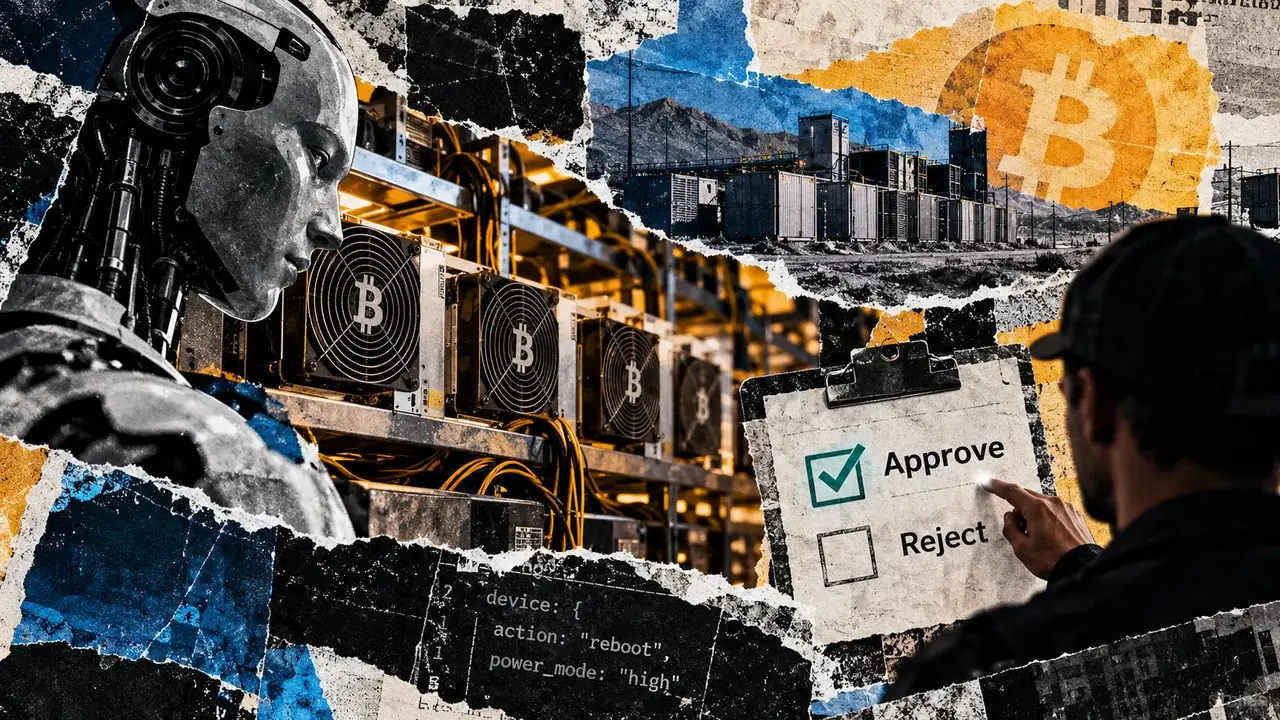
Under the mechanics of Tether’s MDK v0.11 reference agent, device-action tools are designed to pause automatically, holding execution until a designated human operator provides explicit approval. However, implementing this safeguard requires participating mining sites to establish clear policies regarding who is actually entitled to give that green light.
This distinction gained heightened significance as Tether announced widespread commitments from 15 major industry participants on October 24. These companies have pledged to build and maintain integrations with the MDK, an open-source framework engineered to connect disparate mining hardware, mining pools, and backend applications through a unified interface. By establishing a common language, the framework aims to allow software to communicate seamlessly with various systems. Yet, while software integration standardizes communication channels, the authority to execute commands remains entirely dependent on individual site installation, access policies, and configuration choices.
The v0.11 reference release does not inherently dictate which specific code QVAC or individual participating mines have chosen to install on their local networks. Newer iterations found on the project’s main development branch introduce caller restrictions that are notably absent from the v0.11 tag. Consequently, site-level control relies on a combination of factors: who holds the privilege to issue commands and which upstream software version the mining facility has chosen to adopt.
From Integrations to Equipment Commands
The roster of organizations committing to the MDK framework spans a substantial cross-section of the Bitcoin mining supply chain and infrastructure landscape. Tether’s October 24 announcement lists major hardware manufacturers such as BITMAIN, MicroBT, Canaan, and Bitdeer, alongside prominent infrastructure and pool providers including Foundry Digital, Luxor Technology, ACME Swisstech, Elektron Energy, EMCD, F2Pool, Heatbit, OCEAN, Proto, SpiderPool, and Stratum V2.
Under the terms of this collaborative arrangement, participating entities are tasked with building and maintaining specialized software components known as Workers. These Workers function as translators, converting a company’s legacy hardware, mining pool, or system interfaces into the standardized language of the MDK. Each participating organization retains the autonomy to choose which specific functions it exposes to the broader framework. Consequently, external applications can interact cleanly with the common interface rather than requiring developers to engineer custom, separate integrations for every single hardware manufacturer or pool operator.
Tether has highlighted its QVAC mining agent as an early demonstration of the framework, operating natively on the MDK architecture. However, the initial announcement did not disclose specific metrics regarding participating fleet capacity, aggregate shares of the global Bitcoin hashrate, or measured operational efficiencies and savings.
Examining the technical blueprints of the v0.11 reference site reveals how these commands are structured. The reference action tool is configured to accept a single named device and offers two primary operations: executing a hard reboot or modifying the target device’s operating power mode. Power-mode adjustments include low, normal, high, and sleep settings, with the underlying handler systematically verifying whether a given hardware device actually supports the requested mode before dispatching the final command.
These technical capabilities represent the boundaries of the reference example rather than an absolute ceiling on what developers can build using the MDK architecture. Because the reference tool is explicitly classified as a write operation, the agent’s execution loop encounters logic designed to pause when it identifies a tool requiring manual sign-off. Upon reaching this point, the system emits a pending-approval event, halting the process until a human operator responds. If the request is rejected, or if the system times out, the call is blocked. Documentation for the Gateway agent plugin specifies a default two-minute approval window, resulting in automatic rejection if left unanswered.
The v0.11 plugin binds operational sessions and approvals to the specific identity that originally created them. In environments where no user identity is supplied, requests default to a shared local operator profile. Under this shared configuration, the approval pause fails to distinguish between individual human actors.
Therefore, any mining facility assembling an operational environment with this version must actively connect its own internal identity verification systems to the framework’s approval surface. The personnel authorized to view sensitive equipment telemetry and the personnel authorized to approve high-impact power-mode changes require clearly defined permissions established directly by the site operator.
A parallel set of deployment choices applies to data management. The agent reference implementation supports both local QVAC models and externally hosted endpoints. When utilizing a hosted provider, sensitive operational prompts and tool execution results inevitably leave the local mining site and travel to the external endpoint’s host. Running an AI agent locally versus relying on a hosted model represents distinct architectural decisions that site operators must navigate independently.
The Command Path Changes the Permission Check
Security architecture within the MDK framework reveals a distinct split between direct commands and approval-gated actions. Tagged under the v0.11 security blueprint, direct command requests bypass Kernel-side permission checks entirely. In contrast, the separate action push route relies strictly on permissions supplied by an admitted backend caller. This means the Gateway—serving as the primary entry point for applications—must accurately derive permissions from a verified, authenticated user.
Within this architecture, the Kernel coordinates requests smoothly between external applications and internal Workers. While possessing a valid cryptographic key allows a backend process to contact the Kernel and establish basic admission, that key alone does not identify the specific human operator requesting a change.
Further complicating the security landscape, the v0.11 Worker implementation introduces an additional network boundary. Its network command interface historically dispatched requests without validating the caller’s specific key. The tagged security blueprint warned that any network peer capable of reaching a Worker and addressing its public key could theoretically submit commands directly. Whether this exposure poses a real-world risk depends heavily on the network topology and installation practices of the individual mining facility, rather than proving that all mines inherently expose their Workers to external threats. Consequently, securing a reference chat approval does not automatically lock down every route to physical mining equipment unless comprehensive perimeter controls are established around all entry points.
The newer repository code on the main branch addresses several of these early architectural gaps. Code references mapped on October 24 link the v0.11.0 tag to a specific historical commit, while the active main branch points to a more recent snapshot. At this newer snapshot stage, Workers are configured to require admitted caller keys by default, unless an explicit allow-all setting is manually enabled by the operator.
Accompanying changelogs for subsequent versions outline expanded Kernel roles dedicated to reading, writing, and administrative functions, alongside opt-in Machine Control Protocol (MCP) write tools and formal declarations for verifying device state. Yet, official security guides retrieved alongside these updates have occasionally lagged behind repository changes, describing Workers without caller allowlists in their published documentation. This disparity underscores a vital operational requirement: site engineers must carefully audit and match published guidance against actually deployed code before making definitive assumptions about their facility’s security posture.
Release Authority Stays with the Project
A mining facility’s adoption of the MDK also links its operational infrastructure to the project’s broader release governance structure. According to the official MDK governance documentation, ultimate project authority remains with the core team, while the Lead Maintainer holds final technical authority over code merges, architecture decisions, and release planning. Concurrently, the Community Manager retains final authority over strategic direction and project roadmaps.
Crucially, an integration commitment does not grant an external participant any formal authority over MDK software releases. Conversely, holding the authority to merge upstream code does not translate into permission to issue commands inside an operating mining facility.
This division of responsibilities makes regular code reviews an essential ongoing operating duty. The v0.11 security policy clarifies that software fixes are handled on a best-effort basis exclusively for the latest main commit, meaning older commits or tagged releases may not receive retroactive patches. Choosing a specific software version permanently pins a site’s code baseline, while local configuration determines how that code is executed in practice. Subsequent software changes demand independent security evaluations.
The nuanced distinction between accepting a command and confirming the resulting physical state of a piece of hardware illustrates what is ultimately at stake. Having the permission to send a power-mode instruction and possessing verifiable evidence that the ASIC machine successfully achieved the requested operating mode answer entirely different operational questions. Ultimately, a mining operation’s autonomy and security depend directly on who holds the power to approve writes, which backend programs maintain network access to physical equipment, and who controls the adoption of future software updates.