The Russia-linked threat actor known as APT29 has launched a sophisticated, large-scale watering hole campaign codenamed "Poisoned Source," targeting iOS and Android users through compromised legitimate websites, fake domains, and a targeted supply chain attack involving a Ukrainian web analytics service. Discovered by French cybersecurity firm Sekoia in mid-October 2026, the campaign leverages injected JavaScript to profile victims’ devices before delivering platform-specific N-day exploit chains designed to harvest sensitive data, including browser cookies, Wi-Fi passwords, and comprehensive mobile device information.
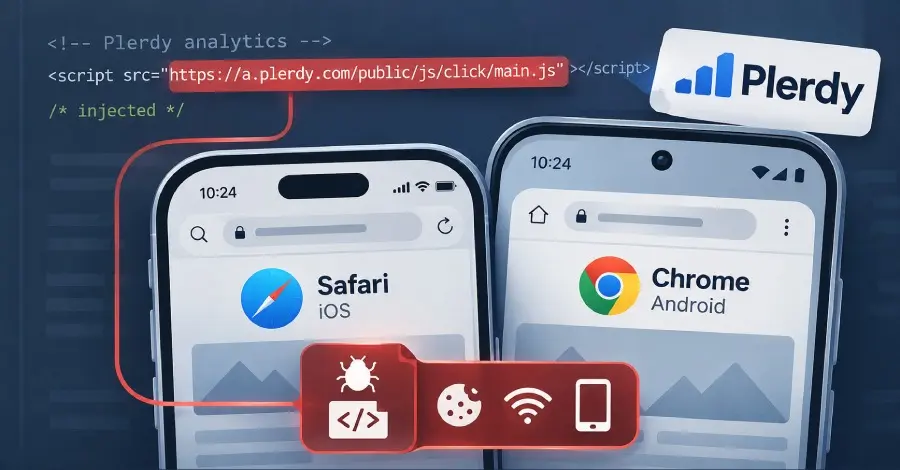
According to a technical report shared with The Hacker News by Sekoia researchers Amaury-Jacques Garçon and Félix Aimé, the malicious activity relies on a multi-vector approach to reach high-value targets. The injected JavaScript code collects browser and device attributes, after which the underlying delivery infrastructure deploys the appropriate N-day exploit chain depending on whether the visitor is using an iOS or Android device. The ultimate goal of the operation is to deploy payloads capable of extracting critical authentication tokens and system details from unsuspecting users.

The campaign’s infrastructure heavily relies on a supply chain compromise affecting Plerdy SEO Tracker, a Ukrainian web analytics service. By infiltrating this service, the threat actors managed to inject malicious scripts into a diverse array of high-profile and sensitive websites. Among the compromised platforms are a major industry trade association representing United States companies operating within the chemical sector, a far-right European political party, and a Bulgarian military-related website. Cybersecurity analysts suspect that rather than casting a wide, indiscriminate net, the watering hole campaign may have been meticulously designed to target specific, strategically important individuals.
Researchers at Sekoia noted that while it remains unclear whether the attackers intended to target visitors to specific websites or sought to compromise as many unpatched mobile devices as possible before selectively filtering information of interest, the choice of compromised sites points to a high-value operational focus. Several of these platforms naturally attract individuals of strategic importance in the context of the ongoing Russia-Ukraine war, as the supply chain attack spread through critical targets such as military websites, special forces portals, and platforms dedicated to military equipment, including ballistic systems and unmanned aerial vehicles.
Regardless of the initial vector or the specific website visited, the attack invariably funnels victims to a standardized JavaScript loader. This component profiles the visitor’s device and web browser before serving the appropriate next-stage malware. For iOS users, the attack chain leads directly to an advanced exploit kit known as DarkSword, which is utilized to harvest browser cookies and deep device data. Meanwhile, Android users face malware equipped to exfiltrate Chrome data and Wi-Fi passwords without establishing permanent persistence on the device.

Intriguingly, the Android component incorporates specific logic to bypass certain hardware. The attack chain features a preliminary check to determine whether the targeted device is a Samsung Galaxy S25 Ultra by examining its specific model identifier, which is SM-S938B. If the device matches these criteria, the exploitation activity is immediately terminated. Data exfiltrated from successful Android compromises is funneled to a centralized telemetry endpoint hosted at "ad.starx-net[.]com:8881/telemetry/v12".
The Android payloads have drawn comparisons to previous threat activity, earning the designation AndroSnitch due to their similarities to ANDROSNATCH. Google previously documented ANDROSNATCH in August 2024 in connection with an earlier APT29 watering hole campaign that targeted Android users visiting a Mongolian government website by leveraging a Chrome exploit chain involving vulnerabilities designated as CVE-2024-5274 and CVE-2024-4671. Security analysts view this operation as further confirmation that state-sponsored intrusion sets continue to reuse commercial surveillance vendor mobile exploit frameworks to lower both the financial cost and technical threshold required to execute advanced mobile operations.
Coruna and DarkSword Kits Evolve

The discovery of the Poisoned Source campaign arrives just weeks after security researchers from iVerify and Report URI detailed the emergence of the P7 variant of the DarkSword exploit kit. This variant has been actively distributed via half-click attacks leveraging commercial ad-based infrastructure. In one observed instance, the exploit was propagated through a malicious Instagram ad themed around the World Cup and served directly from an ad-tracking domain.
Another prominent distribution pathway forms part of a criminal campaign dubbed DeadTag. In this scheme, threat actors acquire expired domains previously associated with legacy analytics and advertising tags that are still actively loaded by thousands of legitimate websites. This allows the operators to silently serve malicious JavaScript to iPhone visitors without requiring any user interaction beyond merely opening the webpage. According to Report URI researcher Scott Helme, the system carefully filters incoming traffic, ensuring that search engines, security scanners, automated browsers, and other bot-like entities receive no malicious content.
Once a legitimate human user visits a compromised page, the script interacts with the attacker’s command infrastructure to determine the appropriate redirection destination. The iPhone exploit paths leveraging the DeadTag network direct victims either to the Coruna exploit kit—traditionally used against older iPhones running iOS versions 13 through 17.2.1—or to the DarkSword P7 kit for devices running iOS versions 18.4 through 18.7.

Security experts emphasize that these mechanisms bypass traditional social engineering traps. Victims do not encounter phishing pages, fake application downloads, or misleading prompts. The exploits attack the browser directly, meaning that simply opening a vulnerable page is sufficient to compromise the device. There is no link to click, nothing to install, and no system warning displayed to the user. If an iPhone is running a vulnerable version of iOS, the kit successfully breaks out of the browser sandbox and installs persistent spyware onto the device.
In addition to state-sponsored espionage payloads, the DeadTag network has been observed directing traffic to a wide variety of secondary schemes, including decoy Google redirects, betting and casino scam sign-up pages, search advertisements for automotive and dental services, and fraudulent survey and prize notification portals. Investigations by Zimperium zLabs indicate that the overall DeadTag network encompasses more than 660 expired and re-registered domains, with over 608 domains actively delivering Coruna-family code as of October 2026.
Although the Coruna framework was originally developed by a sophisticated nation-state actor for highly targeted intelligence-gathering operations, its subsequent leak following initial public disclosures has made the toolkit widely accessible to a broader ecosystem of threat actors for their own criminal and espionage campaigns. Security researcher Santiago Rodriguez noted that contemporary campaigns often utilize lure sites that explicitly instruct visitors to exit their in-app browsers or alternative mobile applications and open the link directly in Safari to ensure the correct operating system conditions are met for the exploit chain to execute.

Targets running iOS 17.2.1 or earlier receive the legacy Coruna framework, characterized by byte-identical JavaScript payloads recovered across multiple configurations. Conversely, devices running later iOS builds receive the newer DarkSword-derived execution chain. The overall distribution footprint spans a diverse array of online properties, including dating portals, artificial intelligence companion platforms, cryptocurrency promotions, media streaming services, and legitimate mainstream websites compromised via hidden iframes, highlighting the pervasive and evolving nature of modern web-based mobile exploitation.