A newly unveiled security system developed by Phylax aims to help decentralized finance (DeFi) protocols intercept and halt malicious transactions before they can settle on the blockchain. While the technology offers a promising shield against sophisticated cyberattacks—such as those orchestrated by North Korean hackers and United States-sanctioned actors—it has simultaneously ignited a debate across the crypto community regarding unintended centralization, smart contract freezing risks, and the delicate balance between security and open availability.
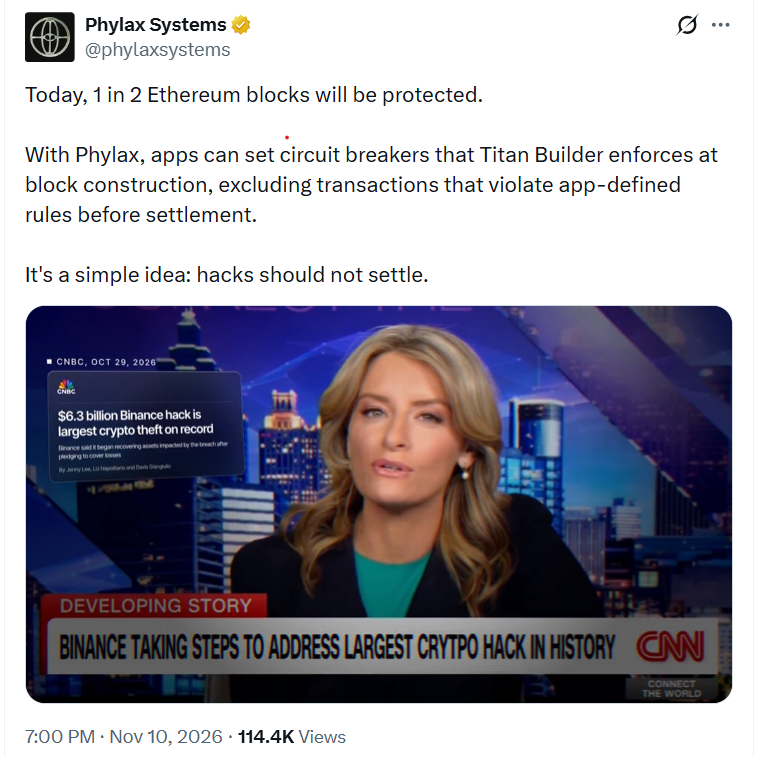
Announced on Nov. 10, the infrastructure relies on a strategic integration with block builder Titan Builder. Under this architecture, Ethereum applications can define specific, customized rules designed to automatically exclude transactions that threaten to produce harmful outcomes during the block construction phase.
Titan Builder, which Phylax reports currently processes roughly one out of every two Ethereum blocks, evaluates incoming transactions against these pre-defined security rules prior to incorporating them into its assembled blocks. The core philosophy of the mechanism is to prevent hacks and exploits from settling entirely, marking a distinct shift away from reactive monitoring systems or emergency interventions deployed only after an attack has already caused severe damage.
“Our mission: stop users from losing money to hacks and errors in DeFi,” the team stated in their official announcement.
A Security Mechanism with a Potential Freeze Risk
In practical terms, Phylax illustrates the utility of the system through scenarios involving vulnerable smart contract architecture. For example, a flawed lending vault might mistakenly release $1 million to a user whose collateral shares are genuinely worth only $1,000. With the Phylax circuit breaker operational, a hard-coded threshold could instantly cap the amount leaving the vault in a single transaction, effectively neutralizing the attempt to drain the protocol’s liquidity pool.
Proponents argue that similar safeguards could have mitigated the staggering losses sustained in recent high-profile security breaches. These include the massive $6.3 billion Binance hack and the $380 million Bitget exploit, both of which saw malicious actors compromise exchange wallets and swiftly funnel immense volumes of digital assets through various decentralized protocols to obfuscate their tracks.
Despite the obvious defensive advantages, digital assets lawyer Gabriel Shapiro has raised notable concerns. Shapiro warned on social media that applications integrating the system could inadvertently become vulnerable to complete freezing if block builders were to suddenly stop providing the mandatory security attestations.
According to Shapiro’s analysis, smart contracts can be configured to systematically reject transactions unless they arrive packaged inside blocks produced by builders that have executed the required checks. Should those validating builders halt their attestation services, the protected protocol functions could continually reject user transactions until the service is restored.
Odysseas Lamtzidis, the founder and chief executive officer of Phylax, countered that protocols can easily mitigate this risk by defaulting to an inclusive operational model when security checks are temporarily offline.
“The sane default we provide and suggest to protocols is a fail-open behavior,” Lamtzidis explained in an interview.
However, Lamtzidis acknowledged that this protective safeguard remains entirely optional, leaving individual development teams to weigh the competing priorities of operational availability and absolute safety. “Some protocols might choose to prioritize safety over liveness,” he noted, adding that protocols retain the ultimate authority to determine whether their smart contracts remain immutable or subject to future governance changes.
Shapiro maintains that fail-open protections ought to be made mandatory by default, and any subsequent modifications to these safety parameters should be subjected to strict time delays to prevent protocols from stripping away protections on short notice.
Ethereum’s Builder Concentration Problem
Beyond the immediate mechanics of circuit breakers, the system has brought renewed scrutiny to Ethereum’s heavily concentrated block-building market.
Ethereum researcher Fan Zhang observed that technology like the one offered by Phylax is only becoming practically feasible because of existing centralization within the block-builder ecosystem. “We finally have a way to implement this effectively,” Zhang noted, “but sadly only because of how centralized Ethereum’s builder market has become.”
While Zhang acknowledged that the approach brings highly appealing security benefits—particularly in an era where automated artificial intelligence bots can discover smart contract vulnerabilities faster than ever—he also warned that introducing auxiliary code at such a critical juncture in transaction processing generates new failure modes. These risks span potential implementation errors as well as the theft, loss, or impersonation of builder signing keys.
“I think the community is very concerned about centralized builders and is making efforts to address them. So I’m concerned that these efforts may undermine each other,” Zhang added.
Echoing these reservations, Ethereum researcher Sen Yang pointed out the commercial implications for the infrastructure market. “If major protocols rely on a small number of builders for security enforcement, this could give those builders a competitive advantage and further exacerbate market concentration,” Yang explained.
Yang noted that while Ethereum’s proposed enshrined proposer-builder separation (ePBS) upgrade, which is slated for inclusion in the upcoming Glamsterdam upgrade, may successfully diminish reliance on third-party relays, it still fails to directly address the underlying concentration within the builder market itself. Nevertheless, Yang observed that transactions excluded by dominant builders could theoretically still find inclusion via non-censoring builders, resulting in temporary transaction delays rather than permanent exclusion.
Where Does Security Become Censorship?
A central point of contention surrounding the Phylax system is whether optional, outcome-driven transaction filtering crosses the line into network censorship.
Phylax maintains that its architecture introduces no new centralized authority over Ethereum transactions because the protocols themselves autonomously define the filtering rules. Lamtzidis emphasized that the technology is explicitly opt-in, comparing the automated security checks to conditional logic already standard in smart contract programming.
“It’s no different than a require() statement,” Lamtzidis said, asserting that true censorship fundamentally implies arbitrary decision-making, external coercion, or force.
Zhang offered a similar distinction between applications voluntarily choosing to filter transactions and external actors forcing censorship onto the network. “Applications willingly signing up for filtering is fine, as a user can walk away from such applications,” Zhang said. “It’s externally forced censorship that’s the problem. That’s where I’ll draw the line.”
Stefanie Boss, co-author of recent academic research examining censorship resistance and compliance behavior within Ethereum’s consensus mechanism, suggested that rules focused strictly on the technical outcome of a transaction are inherently less alarming than rules targeting the identity of the transaction sender.
“In this case, it is also result-driven, which is often considered less risky,” Boss stated. She regards the primary security objective as entirely legitimate, arguing that “the harm of those hacks is much higher than the harm of this type of exclusion.”
At the same time, Boss cautioned that such filtering rules could potentially be repurposed over time to enforce regulatory sanctions or politically motivated exclusions. She emphasized the critical need for proper governance safeguards to guarantee that rule sets remain fair and strictly dedicated to core security purposes.