A series of high-profile cyber incidents has sent shockwaves through the European retail sector this week, forcing major multinational corporations to take emergency measures to secure their networks and protect consumer data. From supermarket chains in the Netherlands to fashion retailers in the United Kingdom, the surge in disruptive activity has highlighted the increasing vulnerability of large-scale retail infrastructures to sophisticated digital threats.
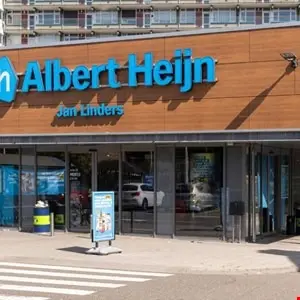
The wave of reports began in earnest on October 12, when Netherlands-based multinational retail giant Ahold Delhaize issued a formal notice confirming that it was contending with a significant "security issue" within its internal networks. The company, which operates an expansive portfolio of grocery and specialty stores, reported that it had been forced to take "some systems offline" as a precautionary measure to prevent the potential spread of a digital intrusion.
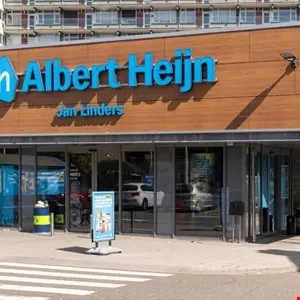
The operational fallout of this move was immediate and wide-reaching. The disruption directly impacted three of the group’s prominent brands: the supermarket chain Albert Heijn, which holds a massive market share across the Netherlands and Belgium; the Dutch drugstore chain Etos; and the specialty liquor store chain Gall & Gall. While Ahold Delhaize has yet to disclose the specific nature of the cyber-attack, the decision to proactively shutter systems suggests a high level of caution aimed at mitigating damage to both company assets and the integrity of customer data.
Expansion of Incidents to UK Fashion Retailers
The concern within the retail sector deepened the following day when it was revealed that the South African retail powerhouse, The Foschini Group (TFG), had also fallen victim to a cyber-related event. According to reports from Reuters, the company became aware of an unauthorized intrusion on October 11, specifically targeting its UK subsidiary, TFG London.
The impact of this incident was localized to specific high-street fashion brands under the TFG umbrella, most notably Phase Eight, Hobbs, and Whistles. As investigations into the scope of the breach commenced, the group sought to reassure stakeholders and customers alike, stating that there was currently "no reason to believe that payment information is at risk" at this stage of the inquiry.
In a strategic display of network resilience, TFG noted that the impact was limited to specific entities. Other high-street brands owned by the group, including Inside Story and White Stuff, remained fully operational and seemingly unaffected. Furthermore, the company confirmed that its major global subsidiaries, TFG Africa and TFG Australia, were operating without any disruption, suggesting that the group’s decentralized IT architecture may have played a role in containing the incident. TFG has since confirmed that it has engaged with relevant UK authorities to manage the aftermath of the breach.
The incident drew commentary from industry experts regarding the effectiveness of corporate digital hygiene. Muhammad Yahya Patel, vCISO and cybersecurity advisor for EMEA at Huntress, pointed to the importance of network segmentation in such scenarios. "The fact that Inside Story and White Stuff within the same group were unaffected, and that TFG’s wider Africa and Australia operations were untouched, suggests some degree of system separation was in place," Patel noted. "That separation, which limited the blast radius, is worth noting as a positive."
As news of these breaches spread, other major retailers began to face scrutiny. Reports in The Times indicated that H&M was investigating circulating rumors of a potential security incident involving its systems. However, at the time of publication, the Swedish retail giant maintained that it had found no evidence of a compromised data environment, characterizing the reports as unsubstantiated. As it stands, there is no formal evidence to suggest that the incidents impacting Ahold Delhaize, TFG, and the rumors surrounding H&M are linked, though the timing of these events has placed the broader retail industry on high alert.
ASOS Navigates Third-Party Platform Intrusion
These recent events are further complicated by the fallout from an earlier security issue involving the UK-based online fashion retailer ASOS. Days before the current wave of reports, ASOS customers were startled to receive an unusual push notification via the company’s mobile application, which contained messages suggesting that the retailer had been compromised.
ASOS subsequently confirmed that the incident was not a direct breach of its primary internal infrastructure, but rather an unauthorized intrusion into "third-party platforms" that the company utilizes for customer communications. The firm acknowledged that personal information, including names, contact details, and certain non-personal account-related data, had been accessed by the unauthorized parties.
In a comprehensive update published on October 13, ASOS sought to quell rising concerns among its customer base. The retailer reiterated that its core systems remained secure and that no payment-card information or account passwords had been impacted by the intrusion. While the company has taken steps to secure its third-party integrations, the incident serves as a stark reminder of the risks associated with the complex supply chains of digital services that modern retailers rely upon to communicate with millions of users.
Broad-Spectrum Risks to Physical Infrastructure
The current climate of retail cybersecurity is further darkened by incidents that extend beyond the digital realm and into physical operations. In France, several major supermarket chains have been grappling with the aftermath of a sophisticated and malicious attack that targeted physical infrastructure rather than just consumer data.
Between the night of October 11 and 12, unknown actors managed to gain access to the refrigeration control systems of multiple supermarket locations. By tampering with these automated systems, the attackers caused significant temperature fluctuations, leading to the spoilage of a massive volume of food products. The financial impact of this incident is estimated to be in the hundreds of thousands of euros, marking a shift toward cyber-attacks that cause direct, tangible economic loss.
This variety of incidents—ranging from the unauthorized access of communication platforms at ASOS to the disruption of internal networks at Ahold Delhaize and the physical sabotage of cooling systems in France—illustrates the diverse threat landscape facing the retail sector today. Retailers are currently forced to defend against a multifaceted threat model where the goal of the adversary may be data exfiltration, service disruption, or even the destruction of physical inventory.
As investigations continue, the retail sector is likely to see a shift toward more stringent cybersecurity frameworks. The reliance on legacy systems, the proliferation of third-party software integrations, and the increasing connectivity of physical hardware—such as refrigeration and security systems—create a broad attack surface that requires constant vigilance. For now, corporations are doubling down on their incident response protocols, working closely with law enforcement and cybersecurity agencies to identify the perpetrators and reinforce their defenses against future incursions. The industry remains in a state of heightened caution, waiting for the full scope of these incidents to be understood and for the necessary safeguards to be implemented across global operations.