The Unseen Insider Risk: Why Your Organization’s AI Agents Need Immediate Governance
Right now, there is likely an autonomous artificial intelligence agent running silently on a laptop somewhere within your corporate network. Operating without direct human oversight, this application stores critical database passwords and API keys, maintains access to sensitive internal systems, and executes tasks in the background.
Nobody on the security team reviewed its access permissions. In fact, nobody truly owns it.
If a human employee operated with that level of unchecked reach and minimal supervision, enterprise security teams would immediately classify it as a severe insider risk. Yet, organizations routinely overlook these autonomous applications, continuing to categorize them strictly as benign productivity tools.
While the broader cybersecurity conversation frequently centers on how external threat actors leverage artificial intelligence for sophisticated attacks, a more immediate and pervasive danger may already reside inside the organization. Unsanctioned and unmanaged artificial intelligence tools are proliferating across corporate environments, creating a massive blind spot for security operations centers that were never designed to track them.
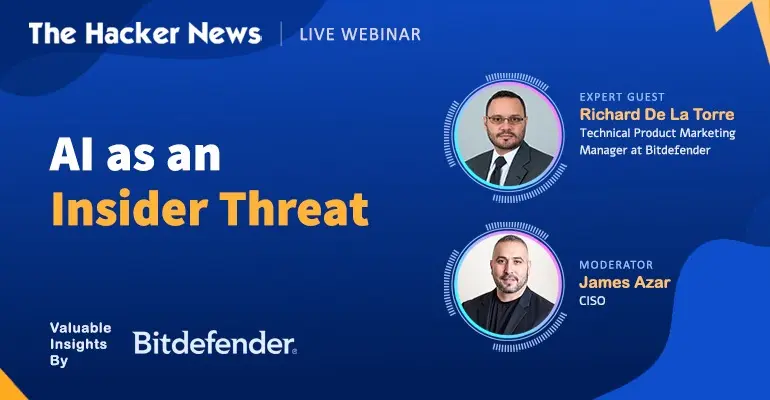
To address this escalating challenge, industry experts are turning their focus toward the hidden vulnerabilities introduced by autonomous technology. A forthcoming webinar titled AI as an Insider Threat: From Shadow AI to Governed AI, featuring expert guest Richard De La Torre, Technical Product Marketing Manager at Bitdefender, aims to provide security leaders with a practical playbook for bringing this unseen artificial intelligence under control before it leads to a costly compromise.
Where AI is Hiding on Your Endpoints
The proliferation of unmanaged artificial intelligence extends far beyond the traditional boundaries of software development teams. Today, a diverse array of advanced digital tools—including autonomous AI agents, intelligent coding assistants, Model Context Protocol (MCP) servers, and specialized browser extensions—are quietly turning up across business units and departments.
Crucially, the vast majority of these applications never cross the corporate network gateway in a way that legacy security tools can recognize. They are installed locally, operate within encrypted sessions, and interact directly with cloud-based endpoints, bypassing the traditional perimeter defenses that chief information security officers have relied on for decades.
This dynamic creates a profound and dangerous irony within modern enterprise environments: the artificial intelligence tools that possess the deepest access to sensitive corporate infrastructure are frequently the exact applications that security teams cannot see. Without visibility into what is running on corporate endpoints, organizations are effectively operating in the dark, trusting that third-party extensions and autonomous agents will behave securely without any form of centralized validation.
The Visibility Gap, By the Numbers
The scale of this blind spot is substantiated by recent industry data. According to Bitdefender’s 2026 Cybersecurity Assessment report, a mere 51.8 percent of organizations report having full visibility into the artificial intelligence tools utilized by their staff on a daily basis. This leaves nearly half of all surveyed enterprises operating without a complete picture of their digital attack surface.
This widespread lack of visibility carries tangible financial and operational consequences. Research conducted by IBM indicates that approximately 20 percent of organizations that suffered a data breach were compromised through shadow artificial intelligence—instances where unauthorized or unmonitored AI tools introduced vulnerabilities or mishandled sensitive data.
These sobering statistics raise a fundamental question for corporate leadership: what can security teams realistically do to mitigate risks they cannot even see? This operational dilemma serves as the core focus of the upcoming Bitdefender webinar, which is designed to demonstrate what lean security teams can accomplish when faced with pervasive shadow artificial intelligence.
From Shadow AI to Governed AI
Recent investigative research conducted by Bitdefender Labs offers a sobering look at what is genuinely running on corporate endpoints, drawing insights from real-world machines analyzed in the wild. Among the findings is the alarming discovery of a malicious agent skill captured in an active environment, underscoring the reality that adversaries are already exploiting the trust placed in autonomous software components.
For many organizations, the instinctive reaction to the rise of shadow artificial intelligence is an outright ban. However, security professionals have repeatedly found that heavy-handed blocking strategies tend to fail, driving employees to find workarounds that further exacerbate the visibility problem.
The viable alternative to prohibition is governed adoption. Security frameworks must evolve to accommodate the legitimate productivity benefits of artificial intelligence while simultaneously establishing strict guardrails, access controls, and monitoring mechanisms. The upcoming expert session aims to illustrate what governed artificial intelligence looks like in daily practice, moving organizations away from reactive panic and toward sustainable risk management.
Addressing the Threat Before Policy Catches Up
The artificial intelligence applications already running on enterprise endpoints will not wait for leadership committees to draft comprehensive corporate policies. The speed of technological adoption consistently outpaces traditional governance models, leaving organizations vulnerable to data exfiltration, credential theft, and unauthorized system access.
As enterprises grapple with the realities of decentralized technology deployment, the need for actionable intelligence and practical security frameworks has never been more acute. Industry professionals seeking to understand the full scope of the challenge and discover methodologies for reclaiming control over their endpoints can register to save their seat for the upcoming discussion on artificial intelligence as an insider threat.