By Ravie Lakshmanan | November 03, 2026
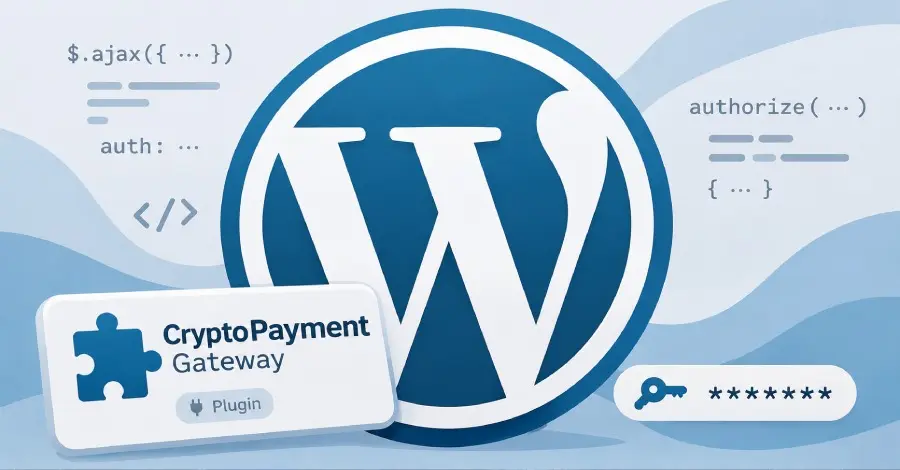
Threat actors have begun actively attempting to exploit an unpatched, maximum-severity security vulnerability in the CryptoPayment Gateway WordPress plugin, according to recent intelligence and public warnings from cybersecurity researchers. The flaw exposes affected websites to severe risks, including unauthenticated file deletion and the potential theft of sensitive financial configuration data.
The security issue, officially cataloged as CVE-2026-81648, carries a maximum base score of 10.0 on the Common Vulnerability Scoring System (CVSS), marking it as critically dangerous. Successful exploitation of this vulnerability permits remote, unauthenticated users to execute administrative operations that they have no business accessing. This unauthorized access can lead directly to the deletion of arbitrary files on the underlying web server and the extraction of highly sensitive information, such as stored cryptocurrency wallet credentials.
Detailed technical descriptions of the flaw highlight a fundamental lack of security checks within the plugin’s architecture. According to the entry published on the National Vulnerability Database (NVD) maintained by NIST, the CryptoPayment Gateway WordPress plugin—spanning versions 1.2.1 to 1.2.2—fails to apply proper authorization validation on one of its AJAX endpoints.
This design oversight leaves the software wide open. It allows unauthenticated visitors to invoke administrative functions, which includes deleting arbitrary files on the server hosting the site, completely overwriting the payment gateway’s configuration parameters, and recovering stored wallet credentials in cleartext format. Because these credentials can include private keys or authentication tokens associated with cryptocurrency transactions, the exposure presents an immediate and catastrophic risk to any funds managed or linked through the gateway.

The vulnerability impacts plugin versions 1.2.1 through 1.2.2, which represents the final iteration of the software. According to tracking data from WP Scan, there are no known patches, hotfixes, or official updates available to remediate the flaw. Recognizing the severity of the security issue, the plugin was officially closed on the WordPress Plugin Directory on August 28, 2026, and removed from public circulation, meaning it is no longer available for download.
Despite its removal and the absence of a fix, historical download statistics indicate that the plugin accumulated a total of 1,845 downloads over its lifespan, including 20 downloads recorded in the final week before its removal. While the exact number of active installations remaining on live WordPress websites at the time of the discovery remains difficult to quantify precisely, security monitoring suggests that enough legacy instances exist to attract the attention of malicious actors scanning the web.
Recent telemetry shared by cybersecurity specialists confirms that these theoretical risks have translated into active, real-world attacks. Researchers at Defused Cyber took to social media to report ongoing malicious activity targeting the vulnerability. In a post shared on the platform X, the research outfit stated that they are actively observing in-the-wild exploitation attempts aimed at exploiting CVE-2026-81648.
Furthermore, the intelligence gathered by Defused Cyber sheds light on the infrastructure being leveraged by the attackers. According to their findings, the malicious requests and scanning traffic recorded against the vulnerability originated from hosting infrastructure that explicitly markets itself as "Anonymous KYC-Free VPS Hosting," highlighting the deliberate steps threat actors take to obfuscate their origins while targeting digital asset infrastructure.
Given the maximum severity of the flaw, the lack of an official patch, and the confirmed presence of active exploitation attempts in the wild, cybersecurity experts and platform administrators are urging immediate defensive action. Website owners who previously installed the CryptoPayment Gateway plugin are strongly advised to remove the software entirely from their environments without delay.
In addition to uninstalling the vulnerable plugin, security practitioners recommend that administrators immediately rotate any wallet keys, API secrets, or credentials that were ever associated with the gateway configuration. Conducting a thorough forensic audit of the server and website files is also encouraged to identify any unauthorized file deletions, unexpected configuration changes, or lingering indicators of compromise left behind by scanning or exploitation scripts operating from anonymous VPS infrastructure.