A newly disclosed critical security vulnerability in the Linux kernel has sent ripples through the cloud computing industry. The flaw allows code executing inside an isolated virtual machine to read memory from the underlying host computer, effectively bridging a boundary that cloud providers have relied upon for decades to keep multi-tenant workloads securely separated.
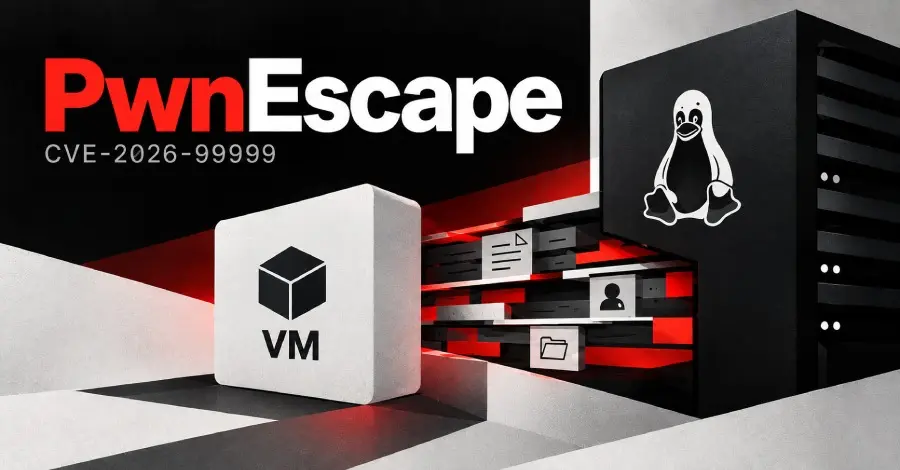
Tracked under the identifier CVE-2026-99999 and nicknamed "PwnEscape," the vulnerability resides deep within the Linux kernel’s core networking code rather than in the specific configuration or deployment architecture of any single cloud vendor. Because the Linux kernel forms the foundational shared layer across vast segments of modern cloud infrastructure, the discovery has implications that extend far beyond the single environment where it was initially demonstrated.
The vulnerability was uncovered as part of a high-stakes security challenge hosted by cloud platform Vercel. Following responsible disclosure practices, the finding was reported privately before any public details were released. According to security advisories and project maintainers, there is currently no evidence to suggest that the flaw has been exploited in the wild by malicious actors or utilized in real-world cyberattacks.
What the Researcher Demonstrated
The vulnerability was discovered by security researcher Paulos Yibelo of the firm pwn.ai. In a detailed technical write-up, Yibelo demonstrated that specially constructed network packets transmitted from within a restricted virtual machine could successfully achieve three distinct outcomes: reading host memory, crashing the host operating system, and executing arbitrary code on the underlying machine. Crucially, all three attack vectors stem from the exact same underlying kernel flaw.
During live demonstrations conducted against Vercel’s production sandbox environments, Yibelo showed that each network packet sent by a guest virtual machine could extract approximately 32 bytes of raw host memory. By maintaining a continuous stream of these crafted packets, an attacker could theoretically harvest ongoing streams of data.
More destructive capabilities, such as triggering a complete host crash and achieving remote code execution, were successfully observed and verified on the researcher’s own laboratory hardware configured to mirror Vercel’s production setup. In those tests, a mere two specially crafted network packets were sufficient to crash a host machine, immediately terminating every isolated sandbox running on that instance. By further leveraging the flaw, the researcher ultimately gained administrative control over the host system, achieving a complete breakout from the virtual machine wrapper. However, Yibelo explicitly noted that this level of host compromise was strictly a controlled laboratory result and not a demonstration of root command execution within any live vendor production environment.
The research itself was accelerated through the use of an advanced AI-assisted security infrastructure known as Omega-Pwn. This internal harness combined custom security tooling with elements of the OmegaClaw architecture, allowing researchers to track hypotheses, analyze complex code traces, evaluate failed attempts, and document experimental results across extended research sessions. A large language model served as the primary reasoning engine, while the human researchers directed the investigation, challenged its analytical outputs, and rigorously validated interesting findings against actual kernel behavior on controlled systems.

Despite the severity of the memory leak, Vercel confirmed through its evaluation of the challenge submissions that no report or exploit demonstration successfully extracted actual customer files, sensitive cryptographic secrets, or proprietary application data from the shared infrastructure.
Severity and Attack Vector Characteristics
Linux kernel maintainers formally assigned the vulnerability the identifier CVE-2026-99999, issuing an initial severity rating of 9.3 out of 10, placing it firmly in the critical category. While the U.S. National Vulnerability Database logged the entry, formal independent reviews by federal databases were still pending as the details circulated.
The official vulnerability record classifies the attack vector as local. In practical terms, this means an adversary cannot exploit the vulnerability remotely by hurling malicious packets across the open internet. Instead, an attacker must already possess the capability to execute code inside a guest virtual machine—such as through a compromised container workload or a malicious user account—before they can begin crafting the packets required to probe the host layer.
Furthermore, the vulnerability does not currently appear on the Cybersecurity and Infrastructure Security Agency’s catalog of known exploited vulnerabilities, reinforcing that the threat has remained contained within research environments thus far.
Why the Flaw Reaches Beyond Vercel
The discovery came to light because Vercel operates a high-density serverless execution model known as Vercel Sandbox. This architecture isolates each individual customer’s code inside its own Firecracker microVM—a lightweight, highly optimized virtual machine running its own dedicated copy of the Linux kernel on top of bare-metal Amazon EC2 host hardware. Under normal operating conditions, this microVM acts as an unyielding physical wall separating a customer’s code from the host machine and from the workloads of other tenants.
The core issue, however, does not lie within the microVM boundary or Vercel’s virtualization layer. Investigators noted that Vercel’s sandbox environment was already hardened significantly beyond standard industry baselines and contained no noticeable misconfigurations. Instead, the vulnerability resides deep inside the native networking stack of the Linux kernel itself.
Because virtually all major cloud service providers and container orchestration platforms rely on the same underlying Linux kernel networking subsystems to manage and separate multi-tenant workloads, any flaw at this level inherently poses a systemic risk to shared cloud infrastructure rather than being an isolated product defect.
The Fix and the Patched Versions
Addressing the root cause required a direct patch to the Linux kernel. A primary fix was authored by Michael S. Tsirkin of Red Hat and merged directly into the mainline Linux kernel tree under commit code 6785011f8b16abf40b1e9d8b2e332232b3e68822. The solution introduces a vital validation check ensuring that packet checksum data cannot incorrectly point into the IPv4 header before the kernel processes the packet. This protective check was implemented across five distinct locations within the kernel’s networking source code.

Kernel developers characterized the change as a defense-in-depth measure, noting that more comprehensive validation regarding how packets initially enter the kernel stack remains an area for ongoing development.
Maintainers quickly backported the security patch into multiple supported stable kernel branches. The first fixed versions released across these active maintenance trees include version 5.10.272 for the 5.10 branch, version 5.15.223 for the 5.15 branch, version 6.1.190 for the 6.1 branch, version 6.6.159 for the 6.6 branch, version 6.12.113 for the 6.12 branch, version 6.18.57 for the 6.18 branch, and version 7.2.11 for the 7.2 branch.
Because modern Linux distributions frequently backport individual security patches into their own proprietary distribution kernels without necessarily altering the primary public version string, systems administrators have been advised to consult their specific operating system vendor advisories to confirm whether the fix has been actively applied to the running host kernel.
Remediation and Industry Response
Mitigating the PwnEscape vulnerability requires administrators to update the host operating system’s kernel to a patched version or an official vendor-supplied build containing the fix, followed by a complete system reboot. Crucially, updating only the internal kernel of guest virtual machines does not remediate the vulnerability, as the vulnerable networking code resides on the physical host. Security advisories outlined no separate software workarounds for environments unable to immediately apply kernel updates.
In scenarios where patching schedules require operational downtime, organizations typically rely on defense-in-depth measures to limit potential blast radii. Vercel highlighted that it maintains rigorous patch management practices for host kernels, disables nested virtualization features, and executes every microVM through Firecracker’s specialized jailer utility. This jailer restricts the microVM execution process to the absolute minimum set of operating system permissions required to function. While these layered safeguards do not patch the underlying kernel bug, they substantially restrict what an unauthorized actor could achieve if an exploit were successfully mounted.
The vulnerability itself was uncovered during a two-week security challenge hosted by Vercel in August, which offered up to $1 million in cumulative prizes to security researchers capable of breaching its sandbox architecture. While no single submission claimed the maximum grand prize, Vercel ultimately distributed $242,000 across 1,285 individual security reports, with the PwnEscape discovery standing out as the sole critical finding of the event.
The incident underscores a rapidly evolving shift in vulnerability research, where security firms increasingly leverage artificial intelligence systems to automate complex code analysis and dramatically shorten the timeline required to discover deeply buried structural flaws in critical open-source infrastructure.