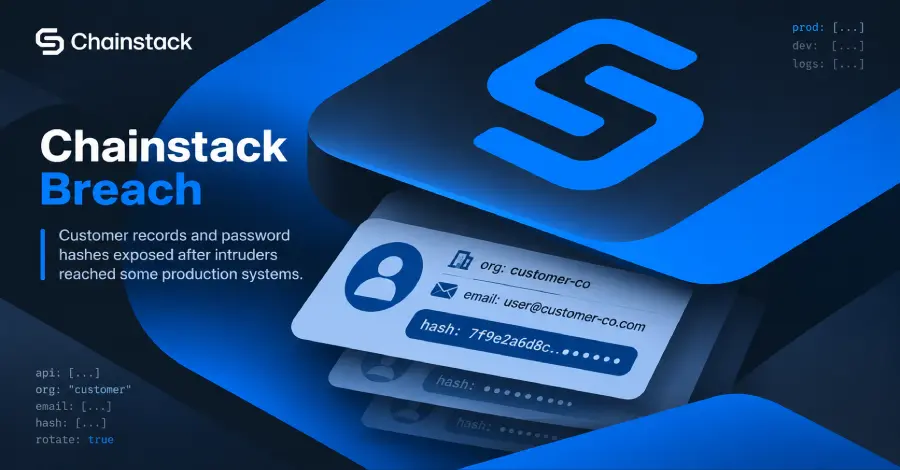
Blockchain infrastructure provider Chainstack has disclosed that it was targeted in a cyber attack, resulting in an unauthorized party gaining access to portions of its internal infrastructure. The security incident is part of an increasingly visible and sophisticated wave of artificial intelligence-driven cyber operations that have recently set sights on high-profile technology and blockchain enterprises.
According to a security advisory published by the company, an external actor managed to infiltrate a development environment on October 26, 2026, before subsequently escalating privileges to breach parts of the production environment. Chainstack’s monitoring systems detected the intrusion on October 31, 2026, prompting immediate incident response procedures that successfully severed the attacker’s access paths on the same day. The company stated that it is actively hardening its systems in the wake of the breach.
The digital intrusion allowed the threat actor to access a database containing customer account details. Specifically, the exposed data includes organization names, individual account holder names, email addresses associated with organization members on the Chainstack platform, and password hashes. Additionally, the attacker gained access to systems holding node credentials. While Chainstack noted it has found no definitive evidence indicating those credentials were actively read or exfiltrated, the company is treating them as compromised as a precautionary measure.
In response to the exposure, Chainstack has strongly urged affected customers to take immediate remedial actions, including rotating their node credentials, regenerating platform API keys, updating account passwords—particularly where passwords may have been reused across multiple third-party services—and remaining vigilant against targeted phishing attempts.

While Chainstack has not publicly detailed the exact technical vectors utilized in the breach, the incident shares strong operational overlaps with a broader, coordinated campaign orchestrated by a China-linked threat cluster. This campaign has been identified as deploying advanced autonomous AI agent frameworks, notably a toolset known as ARTEX, to conduct automated and highly tailored offensive security operations against high-value targets.
WorkOS and Other Major Platforms Targeted by ARTEX Campaign
The disclosure by Chainstack coincides with a parallel security announcement from API platform WorkOS, which revealed that it was similarly targeted in an incident involving the same autonomous AI agent framework. WorkOS discovered the intrusion on October 30, 2026, noting that the unauthorized access was successfully contained within its go-to-market (GTM) systems without spilling over into core production environments or customer platform databases.
Security analysts emphasize that this wave of attacks represents a notable shift in the cyber threat landscape. Rather than relying entirely on manual exploitation, threat actors are increasingly deploying AI-powered agents capable of autonomously devising customized attack strategies, rapidly scanning for vulnerabilities, and automating complex phases of an intrusion.
Commenting on the shifting tactics, WorkOS noted that the integration of artificial intelligence into offensive operations significantly accelerates the speed and scale at which attackers can exploit common weaknesses, such as exposed applications and stolen credentials. This evolution underscores a critical demand for modern organizations to implement real-time monitoring and rapid remediation frameworks capable of instantly correlating suspicious activities across fragmented enterprise systems.

The scope of the ARTEX campaign extends well beyond Chainstack and WorkOS. Last week, prominent blockchain analysis firm Chainalysis also confirmed that it detected an external actor utilizing offensive agentic techniques to compromise its internal systems and specialized tools. As an immediate protective measure, Chainalysis proactively took its Reactor and Data Solutions products offline on November 2, 2026, while continuous monitoring remains in place to detect any further anomalies.
Further illustrating the broad impact of this threat actor cluster, the Dutch Institute for Vulnerability Disclosure (DIVD) fell victim to an ARTEX-linked breach on September 21, 2026. That particular incident involved the exploitation of two critical zero-day vulnerabilities within the open-source Zammad ticketing system, tracked as CVE-2026-102489 and CVE-2026-102490. The successful exploitation allowed the attackers to achieve privilege escalation, execute arbitrary remote code, and exfiltrate sensitive data from the organization’s infrastructure.
As cybersecurity researchers continue to analyze the telemetry surrounding these synchronized incidents, affected organizations across the technology and blockchain sectors are accelerating audits of their development pipelines, API security controls, and third-party vendor integrations to defend against the accelerating adoption of AI-driven cyber weaponry.