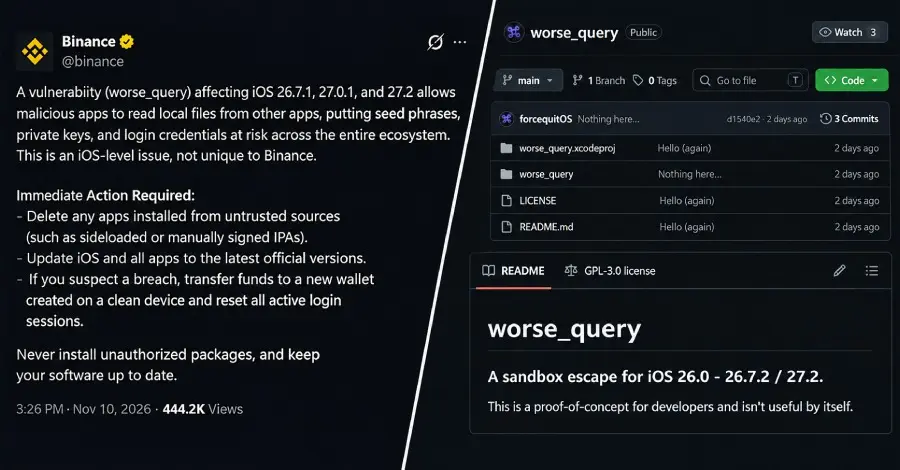
Cryptocurrency exchange Binance has issued an urgent security warning to its users regarding a newly disclosed iOS sandbox escape vulnerability. The security flaw, which was published publicly on GitHub, allows malicious applications to read files belonging to other apps on iPhones running iOS 26 and iOS 27. According to the exchange, this architectural vulnerability places critical data at risk, including seed phrases, private cryptographic keys, and sensitive login credentials. Apple released software updates for both iOS 26 and iOS 27, but the official release notes for these updates do not list a fix for the sandbox escape.
The security issue stems from a proof-of-concept exploit known as "worse_query," which was released on Sunday by a security researcher who goes by the online alias forcequit. The code was published just a day before Apple rolled out its latest operating system updates. At the time of the disclosure, neither Binance nor the researcher had reported any active exploitation, attacks, or cryptocurrency thefts involving the vulnerability in the wild.
In response to the risk, Binance urged users to exercise extreme caution with third-party software, advising them to delete any applications installed from untrusted sources. This includes sideloaded applications or manually signed binaries that operate outside the standard App Store review pipeline. Furthermore, the exchange recommended that users ensure their devices and all installed applications are running the latest available software versions. Because no official patch confirming a fix for the sandbox escape has been verified, the advisory remains a critical preventative measure for high-risk users.

For individuals who suspect their devices or accounts may have been compromised, Binance’s security warning outlines strict remediation steps. Affected users are advised to transfer their digital funds immediately to a new cryptocurrency wallet generated on an entirely clean and verified device. Additionally, users should reset all active login sessions across their accounts to invalidate any potentially hijacked authentication tokens.
The technical mechanism behind the exploit allows the proof-of-concept code to access every application’s data container on an affected iPhone, as well as specific system-level directories on devices running iOS 27. To leverage the vulnerability successfully, an application must first establish an App Group container. The original researcher noted that the base code is primarily intended for developers and is not inherently useful as a standalone attack vector. However, other developers have quickly built user-facing applications on top of the framework that regular individuals can install.
One prominent example of software built using the exploit is WQ Files, a file manager utility developed by Christoph Kolbicz. Constructed directly on top of the worse_query framework, WQ Files can access the data containers of other applications without requiring a jailbreak or a kernel exploit. The utility possesses the capability to edit, delete, and clear data stored by other applications on the device.
WQ Files is designed to be installed via third-party sideloading tools such as AltStore and SideStore. These utilities automatically generate the required App Group when paired with an Apple ID during the installation process. Neither the original researcher nor the third-party developers have clarified whether an application distributed through the official Apple App Store could theoretically leverage the worse_query vulnerability.

The specific versions of Apple’s operating systems mentioned in Binance’s security warning align with the environments tested and documented in the release notes for WQ Files. While the file manager’s developers explicitly tested certain iterations, the original researcher referenced a broader scope of affected firmware versions. Among the various developer and jailbreak communities responding to the disclosure, developers of the jailbreak utility Erosion noted support for iOS version 27.2.1 in a recent repository update. The commit included a note indicating confidence in support for that specific build, which was released by Apple just days prior.
Apple’s updates, designated as iOS 27.2.1 and iOS 26.7.3, officially addressed a pair of high-profile iMessage flaws alongside several underlying Bluetooth vulnerabilities. However, the official support documentation and security notes published by Apple for both iOS 27.2.1 and iOS 26.7.3 make no mention of worse_query or any associated sandbox containment issues. Apple maintains a long-standing policy of not disclosing, discussing, or confirming security vulnerabilities until its internal investigations are complete and a reliable patch or software release is publicly available to users.
Addressing the timeline of the disclosure, the researcher forcequit explained in a public reply on social media platform X that the early release of worse_query was not part of his initial plan. He stated that the publication was expedited because Apple was stalling on responding to his vulnerability reports while community members began experimenting and speculating with early builds of the code.
To date, neither Binance, the original researcher, nor the creators of the derivative applications built on the worse_query framework have publicly named specific cryptocurrency wallet applications that are directly exposed to the sandbox escape. Security analysts continue to monitor the situation as the developer community awaits an official technical response or software patch from Apple to address the underlying sandbox architecture limitations.