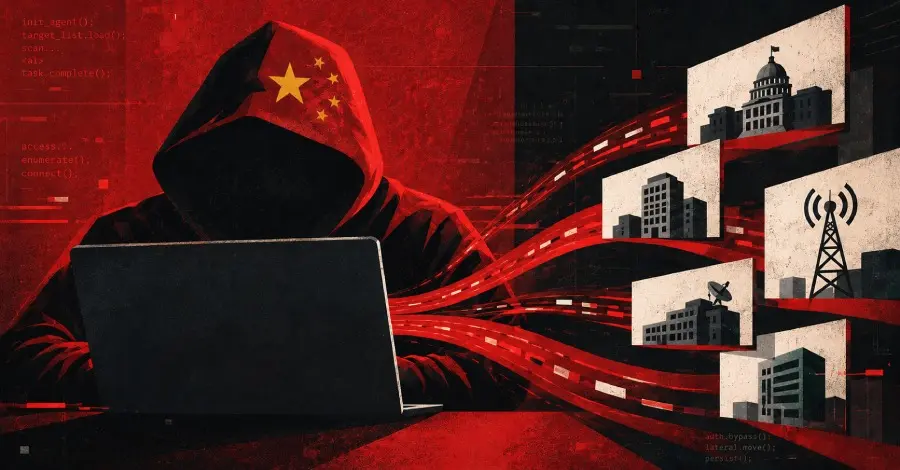
Chinese state-sponsored threat actors have dramatically scaled up their cyber espionage operations, utilizing an advanced Go-based, artificial intelligence-powered penetration testing framework known as ARTEX to strike high-value targets across the globe simultaneously.
The sophisticated campaign has been attributed by cybersecurity firm CrowdStrike to a China-based targeted intrusion adversary tracked under the moniker Vapor Panda, previously known as VexatiousTemper. First identified by security researchers in February 2021, the hacking collective shows significant operational overlap with a threat cluster previously detailed by Trend Micro under the name Earth Estries.
In a recent analysis, CrowdStrike highlighted how the adoption of autonomous, agentic tooling fundamentally changes the dynamics of state-sponsored cyber operations. According to the cybersecurity firm, agentic software like ARTEX enables a massive expansion of operations at unprecedented speed. This allows a relatively small team of human operators to pursue a much wider target set than traditional manual operations could ever support, rather than signaling a wholesale departure from the adversary’s established mission of access development.
The automated onslaught began in earnest on October 17, 2026. Since that date, Vapor Panda has reportedly deployed the artificial intelligence tool against more than 200 distinct organizations worldwide. The sprawling list of victims includes foreign ministries stationed across Latin America, Europe, Asia, and the Middle East, as well as critical defense, semiconductor, and think tank organizations in the United States, alongside telecommunications providers operating in multiple regions.
Following initial automated breaches, post-exploitation activity has been confirmed at nine targeted organizations. These successful intrusions allowed the threat actors to deploy BLOODALCHEMY—a specialized derivative of the infamous ShadowPad malware family—subsequently followed by aggressive credential spraying, network reconnaissance, and internal network scanning. Furthermore, Vapor Panda has conducted password-spraying and credential-scanning activities against at least 12 additional high-value targets, including prominent U.S.-based think tanks and European government entities.

The Inner Workings of the ARTEX Framework
Central to Vapor Panda’s recent global campaign is the deployment of the ARTEX framework, which integrates DeepSeek and an as-yet-unknown subscription-based commercial large language model. This technological architecture allows the threat actors to conduct intrusions at a staggering scale. The system relies on an integrated army of planner and worker agents that communicate and coordinate with one another dynamically to achieve a common strategic objective: moving smoothly from initial system access through host reconnaissance and lateral movement.
Despite the heavy automation, a human operator remains in the loop to oversee the lifecycle of the operation. This human handler directs the autonomous agents to perform high-stakes tasks such as writing web shells, extracting domain administrator passwords, and enumerating endpoint sensor coverage to avoid detection.
The sheer scale of computational activity required for these automated maneuvers is immense. CrowdStrike noted that during a single intrusion, Vapor Panda’s planning agents consumed roughly 1.4 billion input tokens. This staggering consumption highlights the massive scale of automated activity at play and implies even higher token usage across the entirety of the broader campaign.
Unlike older campaigns where artificial intelligence was used merely to assist with individual, isolated digital break-ins, the deployment of ARTEX represents a profound evolution. It operates at a significantly higher strategic level, allowing threat actors to run multiple complex engagements concurrently. The human operator steps in only to steer the autonomous agents toward their ultimate objectives while actively implementing countermeasures to bypass sophisticated endpoint detection and defense mechanisms.
An analysis of recovered operational transcripts underscores how ARTEX combines artificial intelligence with tried-and-tested intrusion techniques. CrowdStrike explained that across these engagements, the autonomous agents pursued multiple parallel attack paths simultaneously, successfully spanning web applications, cloud services, container environments, Active Directory architecture, and mail and virtual private network infrastructure. When a specific attack path failed, the agents seamlessly shifted to alternative approaches. This breadth of capability enables a single human operator to apply a wider range of attack techniques against significantly more targets at once than would ever be feasible through traditional manual operations.

The emergence of ARTEX has sent shockwaves through the cybersecurity community. The tool has witnessed remarkably broad adoption among various threat actors in an extraordinarily short span of time. This rapid proliferation ultimately prompted its developer, Li Puhua—also known as "Autumn-27"—to pull the project and take it completely closed source.
Security researchers at Zscaler ThreatLabz published a report noting that the framework orchestrates multiple large language model backends to autonomously execute reconnaissance, vulnerability identification, and exploitation, thereby significantly lowering the technical barrier required to conduct complex, multi-stage intrusion campaigns.
One of Many Panda Threat Clusters
The public disclosure of Vapor Panda’s AI-driven campaigns coincides with broader findings regarding the expansive threat landscape linked to Beijing. CrowdStrike’s recent threat hunting and legal threat landscape reports have brought to light four previously undocumented, China-linked state-sponsored threat groups: Hollow Panda, Overcast Panda, Titan Panda, and Veiled Panda. These collectives have systematically targeted a broad range of global sectors primarily for intelligence gathering and intellectual property theft.
Among these newly highlighted clusters, Overcast Panda has emerged as one of the most operationally sophisticated and persistent threats facing organizations whose personnel travel frequently to China. This group has been directly linked to close-access intrusions where adversaries deploy their proprietary FlowCloud backdoor onto victims’ personal and professional devices via direct physical access while those targets are physically present in the country.
The FlowCloud backdoor is launched using advanced DLL sideloading techniques, with its internal components meticulously designed to fly completely under the radar and actively resist digital forensic analysis. Command-and-control communications are maintained by leveraging legitimate cloud infrastructure in an ongoing attempt to obscure the attackers’ digital footprint. According to CrowdStrike, FlowCloud is a sophisticated, purpose-built tool uniquely associated with Overcast Panda, providing the adversary with persistent, covert remote access that enables keylogging, screen capture, file collection, and extensive credential harvesting.

Meanwhile, Titan Panda has focused its efforts on a different vector, targeting legal billing software by exploiting a hard-coded Internet Information Services machine key vulnerability within the Intapp Time Server. This flaw allowed the threat actors to achieve remote code execution across multiple prominent law firms.
First detected in April 2026, these attacks resulted in the deployment of an in-memory framework known as IceGiant to conduct reconnaissance, establish persistence, facilitate lateral movement, and execute data exfiltration. Investigators assess that Titan Panda has been actively operational since at least 2021, quietly compromising several legal organizations across North America for over two years.
While the exact method by which Titan Panda managed to acquire the default machine keys remains unknown, security analysts suggest that a prior compromise of a legal entity’s Internet Information Services running the Intapp Time Server may have exposed hard-coded keys within application configuration files. This exposure likely enabled subsequent ViewState deserialization attacks against any organization running default software installations.