The security flaws were discovered in bitcoinjs-lib, a foundational and widely utilized JavaScript library relied upon by developers to build diverse Bitcoin applications, wallet interfaces, and transaction-handling services. According to official security disclosures published on Oct. 26, the vulnerabilities can cause software applications to severely understate the actual miner fee a valid transaction would incur if it were successfully broadcast to the network and accepted by miners.
To address these security gaps, the library’s maintainers have released patches across multiple active release lines, updating the software to versions 5.2.2, 6.1.9, and 7.0.4. The core of the issue centers around the handling of Partially Signed Bitcoin Transactions, commonly referred to as PSBTs. Defined under BIP 174, the PSBT format provides a standardized method for passing transaction data, partial signatures, and metadata between different clients and signing devices. Within this framework, operations such as signing, combining signatures, finalizing inputs, and extracting the final transaction are treated as distinct functions—even when a single application or script executes several of these steps sequentially.
The inherent risk primarily affects third-party applications that import these vulnerable packages and blindly trust the library’s internal fee calculation algorithms or excessive-fee safeguards. If developers do not independently audit and verify the underlying outputs being spent, their software can become vulnerable to unexpected financial drain. Consequently, application maintainers across the ecosystem have been urged to thoroughly review their dependency versions and re-evaluate how their systems ingest and validate imported PSBTs before execution.
Why Valid Signatures Can Accompany Misleading Fees
In the architecture of the Bitcoin network, a transaction fee is fundamentally calculated as the difference between the aggregate value of its inputs and the aggregate value of its outputs. Therefore, if a software implementation understates or misreads an input value, the resulting calculated fee will appear deceptively small, masking the true economic cost of the transaction from the user or the application interface.
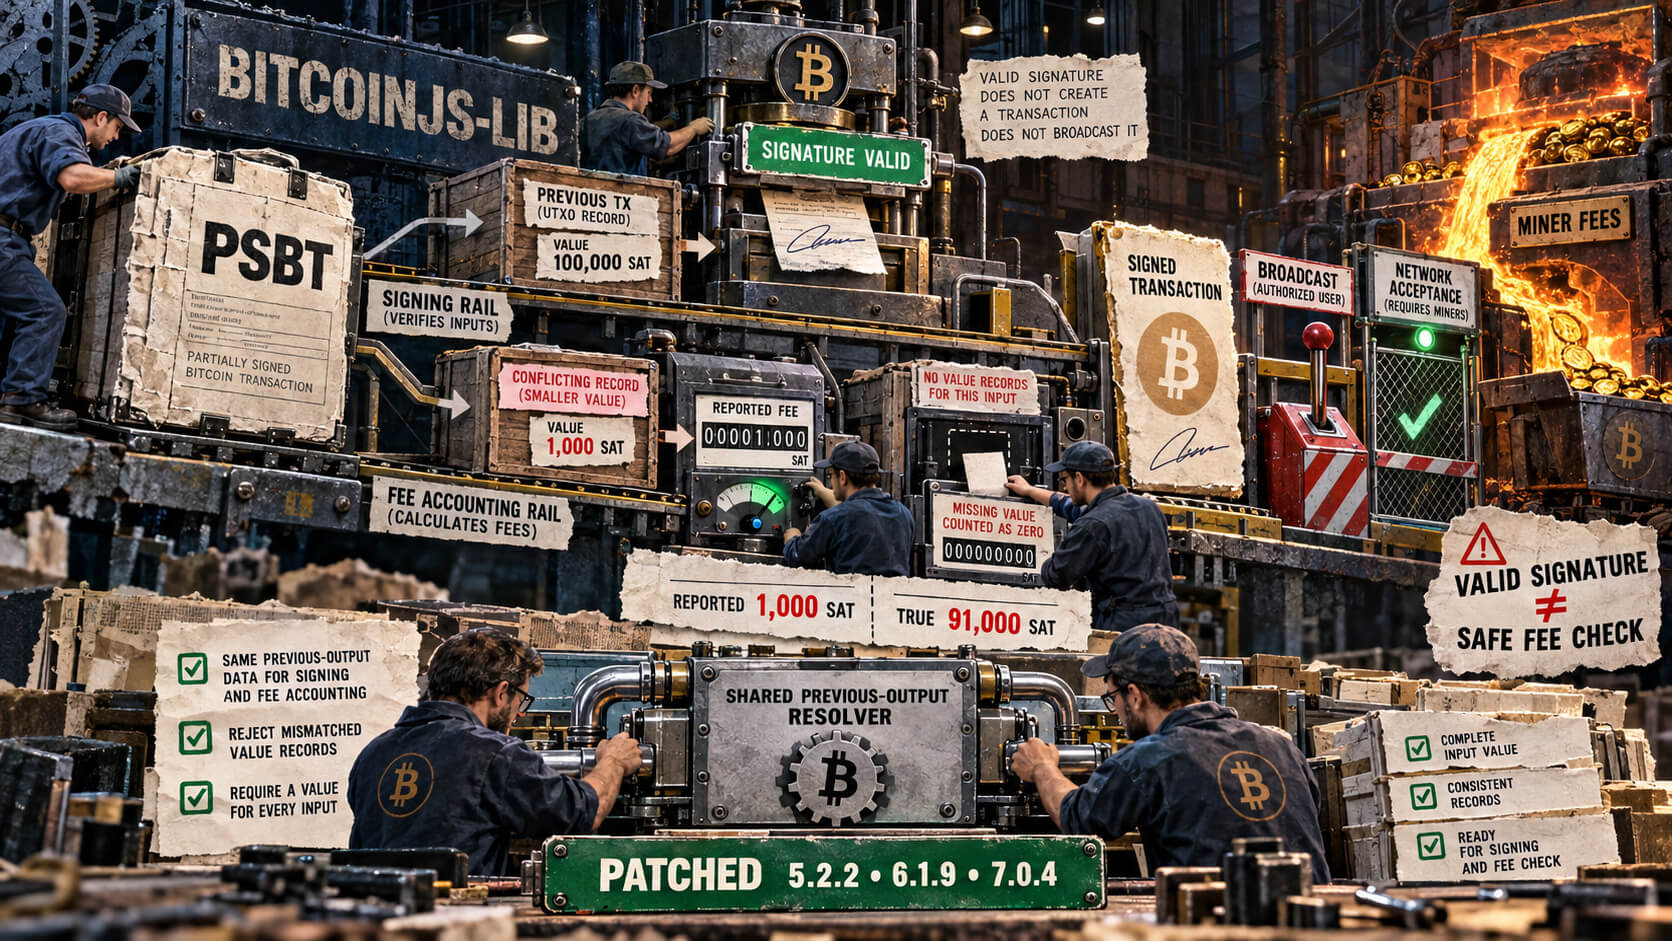
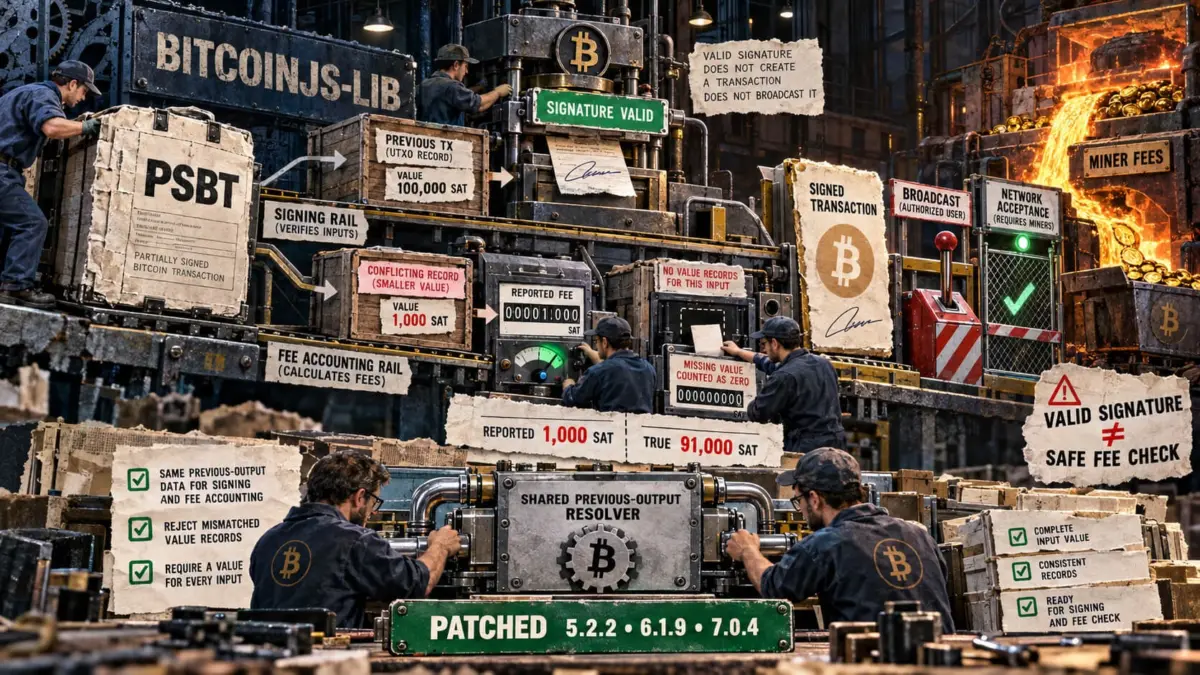
The first major flaw identified in the advisory stems from a dangerous discrepancy between signing routines and fee accounting logic. In vulnerable versions of the library, signing mechanisms and fee calculations could utilize completely conflicting values for the exact same input. While the signing process correctly evaluated the full previous transaction, the separate fee accounting routine favored a conflicting record containing a substantially smaller value. As a result, the vulnerable software was able to authorize and sign the legitimate transaction while simultaneously evaluating an incorrect, drastically lower fee.
To demonstrate the severity of this discrepancy, the advisory outlined a test performed on version 7.0.1 of the library. In this simulation, the actual transaction fee amounted to a staggering 900,000,000 satoshis, yet the vulnerable library erroneously reported a negligible fee of just 200 satoshis. Crucially, the cryptographic signature verified successfully, and the transaction extraction process completed without triggering the software’s default fee-rate warning mechanisms, leaving users entirely unprotected against severe capital loss.
The second advisory highlights a similarly dangerous scenario involving finalized inputs where essential input-value records are entirely missing. In these instances, the internal fee calculator defaults to counting those unvalued inputs as zero. Because an already-signed PSBT can be imported from an external party, it can easily reach this faulty calculation phase without requiring any additional signing operations on the receiving end.
In a hypothetical demonstration of this second bug, a true transaction fee of 91,000 satoshis was reported as a mere 1,000 satoshis by the flawed software. This occurs because finalized scripts and valid signatures alone do not inherently establish or verify the missing value of an input unless explicitly checked.
Network Realities and Remediation Steps
It is important to understand that actual financial loss resulting from these bugs requires an authorized, cryptographically valid transaction to be formally broadcast to the network and accepted into a block. The software defects themselves do not spontaneously create or forge valid signatures; rather, any excess value left unaccounted for is simply absorbed by miners as an exorbitant transaction fee.
Regarding the scope of the affected versions, the conflicting records flaw impacts versions 5.2.0 through 5.2.1, versions 6.0.0 through 6.1.8 including the 6.1.0-rc.0 pre-release, and versions 7.0.0-rc.0 through 7.0.3. Meanwhile, the missing-record vulnerability spans the same v6 and v7 ranges, while also affecting versions 5.1.0 through 5.2.1 within the v5 release line.
The official remediation code addresses these vectors by establishing a unified, shared method for resolving previous outputs between both the signing and accounting modules. The updated code actively rejects conflicting values or mismatched scripts and enforces a strict requirement that a valid amount must be present for every single input during the fee calculation process. Furthermore, the patches ensure that cached fees and extracted transactions are automatically cleared whenever relevant metadata is modified or combined.
For application maintainers and developers who are currently unable to upgrade their dependencies immediately, security experts recommend implementing rigorous independent verification of all referenced output values. Systems should be configured to explicitly reject conflicting records before any signing takes place or fees are trusted, and every individual input value must be independently verified prior to authorizing fee displays or extracting final transaction data.