Artificial intelligence company Anthropic has shed light on a decades-old cryptographic mystery, announcing that its Claude AI system successfully reconstructed the public seed behind P-256—a curve standardized by the National Institute of Standards and Technology that is heavily relied upon for Ethereum passkey signing. The discovery provides wallet developers and cryptographers with fresh insight into the origins of a mathematical standard that has faced scrutiny and suspicion for more than twenty-five years due to its opaque and unexplained genesis.
The finding centers on the public seed, an initial design input used by cryptographers to derive a critical coefficient in the mathematical equation defining the elliptic curve. This public seed is entirely distinct from the private signing credentials that individual users rely on to authorize transactions or manage wallet activity. For decades, the unexplained nature of the seeds originally supplied by the United States National Security Agency fueled widespread skepticism and concern within the cybersecurity community, with many experts whispering about the theoretical possibility of deliberately weakened parameters or hidden backdoors built into government-backed cryptographic standards.
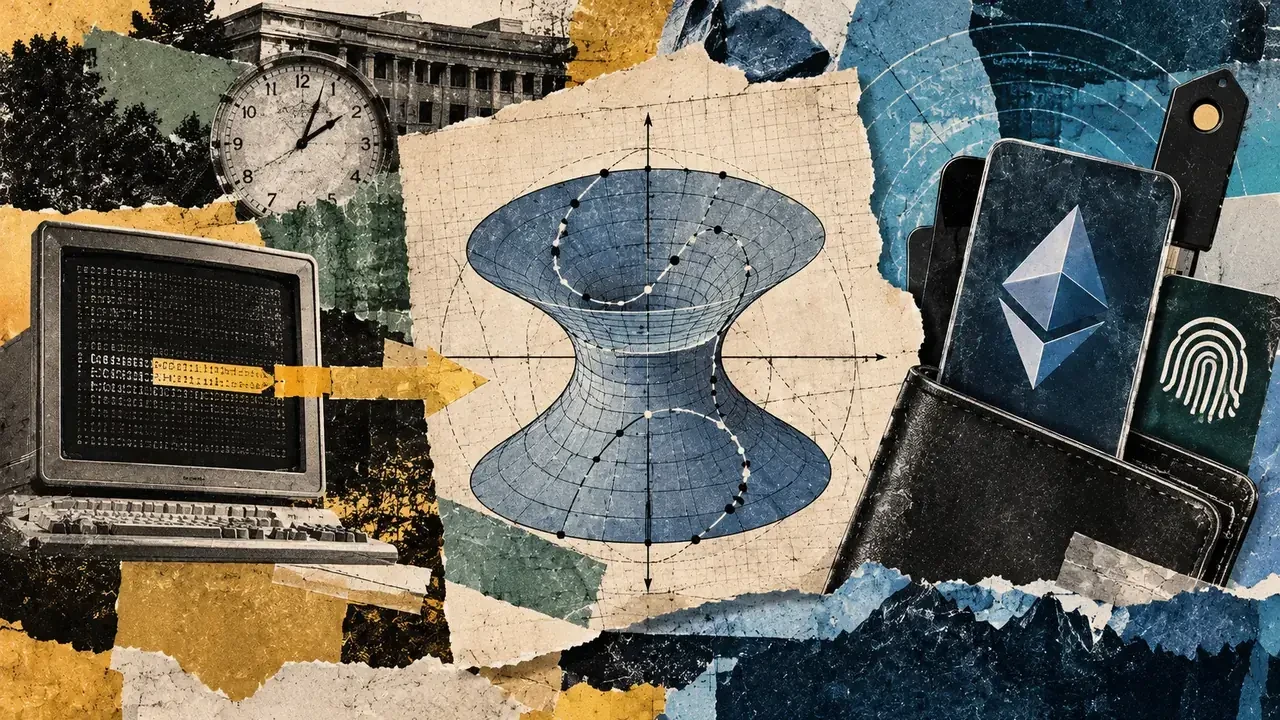
According to Anthropic, the breakthrough came after using Claude to reconstruct a precise recipe for the public constant. The published methodology involves initializing an old C-library pseudorandom number generator, specifically lrand48, using a very specific historical timestamp: August 16, 1997, at precisely 01:52:34 UTC. When this generator runs, it produces a sequential series of candidate seeds. Upon advancing through the sequence to candidate 1,842, the system yields the exact published P-256 value, effectively offering a reproducible recipe for a constant that had previously lacked a transparent historical paper trail.
Anthropic noted that this newfound reproducibility significantly diminishes the plausibility that the curve was designed with deliberate, malicious backdoors. At the same time, the company emphasized that the discovery does not describe any new attack vector, nor does it expose any underlying weakness in the curve itself. Consequently, everyday crypto users and wallet holders need to take no action regarding their security setups.
The relevance of this cryptographic curve to the broader blockchain ecosystem runs directly through Ethereum Improvement Proposal 7951, commonly known as EIP-7951. This specific proposal outlines the technical standards for verifying cryptographic signatures that utilize P-256, which is also widely recognized by its alternative designation, secp256r1. The integration impacts a wide array of modern consumer hardware and authentication mechanisms, including the Apple Secure Enclave, the Android Keystore, and standard FIDO2/WebAuthn hardware authenticators. By bridging these technologies, EIP-7951 effectively connects traditional web-to-device wallet authorization with the high-security signing capabilities already embedded natively within millions of user devices.
The underlying motivation detailed within EIP-7951 highlights several long-standing goals for account abstraction within the Ethereum network. These include enabling seamless device-native signing, facilitating robust multifactor authentication, and simplifying overall key management for end users. Ethereum’s core account documentation maintains a strict distinction between the private keys that securely sign outgoing transactions and the public information utilized by the network to verify those signatures, while contract accounts remain strictly governed and controlled by executable code.
Under the operational framework proposed by EIP-7951, a specialized function known as P256VERIFY takes a message hash, a signature, and a public key, subsequently performing automated checks to validate the authenticity of the signature. Security experts reiterate that the publicly reconstructed seed identified by Anthropic’s analysis remains entirely separate from these sensitive private signing credentials, ensuring that the fundamental security architecture of individual user wallets remains uncompromised.
It is also worth noting that P-256 is mathematically distinct from secp256k1, the elliptic curve that Ethereum has traditionally utilized for its native account management and transaction signing. Therefore, the implications of this discovery are specifically relevant to P-256-compatible signing workflows and passkey integrations, rather than impacting every single Ethereum wallet across the board.
Despite the breakthrough provided by identifying the 1997 timestamp and candidate 1,842, certain historical questions regarding the curve’s complete lineage remain unanswered. Anthropic reported during its research that candidate 876 also yielded a valid prime-order curve of the required mathematical size, leaving the exact selection criteria used by the original designers somewhat ambiguous. Furthermore, the precise number of generation runs performed during the curve’s initial creation, as well as the exact origin of P-256’s base point—a separate, fixed mathematical coordinate required for cryptographic operations—remain unknown to this day, leaving a few lingering chapters in the long history of government-standardized cryptography.