A series of significant cybersecurity incidents has rippled across the European retail landscape this week, causing operational paralysis for several multinational corporations and raising urgent questions regarding the resilience of digital supply chains and customer-facing infrastructure. While there is currently no evidence to suggest that these separate events are coordinated or linked, the concentration of disruptions has cast a spotlight on the vulnerability of large-scale retail networks to malicious actors.
Ahold Delhaize and TFG Among Major Retailers Facing System Outages
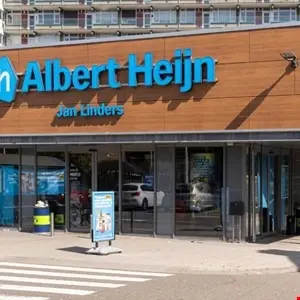
On October 12, the Netherlands-based retail powerhouse Ahold Delhaize issued a formal statement confirming it had been targeted by a security breach. The multinational giant, which manages an extensive portfolio of grocery and pharmacy brands, reported that it had identified a "security issue" within its internal network infrastructure. In a swift, precautionary response, the company opted to take several key systems offline to prevent the potential spread of the threat and to secure its digital perimeter.
The operational impact was felt immediately across several of the group’s flagship brands. Albert Heijn, the prominent supermarket chain operating throughout the Netherlands and Belgium, confirmed disruptions alongside the Dutch drugstore chain Etos and the liquor retailer Gall & Gall. While Ahold Delhaize has yet to provide granular details regarding the nature of the intrusion, the decision to force systems offline suggests a deliberate effort to mitigate a ransomware or data-exfiltration attempt, a standard procedure in modern incident response to isolate affected segments of a corporate network.
The retail sector’s troubles were compounded the following day when reports surfaced concerning the South African retail group The Foschini Group (TFG). On October 13, it was confirmed that the company was actively investigating a cyber incident that had compromised its UK subsidiary, TFG London. According to reports, the breach was first detected on October 11 and directly impacted the digital operations of several high-street fashion brands under the TFG umbrella, specifically Phase Eight, Hobbs, and Whistles.
TFG acted quickly to reassure customers and stakeholders, stating that at this stage of the investigation, there is "no reason to believe that payment information is at risk." The company also clarified that the scope of the incident appeared contained. Notably, other high-street brands within the group, such as Inside Story and White Stuff, remained operational and unaffected. Furthermore, the parent company confirmed that its extensive operations in Africa and Australia continued to function without any disruption. TFG has since notified the relevant UK regulatory and law enforcement authorities, initiating a formal investigation into the breach.
The incident at TFG drew commentary from industry experts regarding the importance of network architecture in limiting the fallout of such attacks. Muhammad Yahya Patel, vCISO and cybersecurity advisor for EMEA at Huntress, observed that the limited nature of the disruption provides a case study in effective IT governance. "The fact that Inside Story and White Stuff within the same group were unaffected, and that TFG’s wider Africa and Australia operations were untouched, suggests some degree of system separation was in place," Patel noted. "That separation, which limited the blast radius, is worth noting as a positive."
As the retail sector grapples with these active incidents, the industry remains on high alert. The Times reported that the Swedish retail giant H&M is also currently conducting an internal review following online speculation regarding a potential breach. As of the time of writing, however, the retailer has maintained that it has found no evidence to suggest that its internal data environment has been compromised or accessed by unauthorized third parties.
Contextualizing the Retail Cybersecurity Landscape
These recent incidents do not exist in a vacuum; they follow a series of high-profile security challenges that have plagued the retail sector throughout the month. Just days prior to the disruptions at Ahold Delhaize and TFG, the UK fashion retailer ASOS found itself at the center of a security controversy after customers reported receiving highly irregular push notifications via the company’s mobile application. The notifications suggested that the retailer had been the subject of a successful hack.
ASOS eventually confirmed that an unauthorized party had gained access to third-party platforms used by the company to communicate with its customer base. The breach resulted in the exposure of personal information, including names, contact details, and certain non-personal account-related data. However, in an updated statement released on October 13, ASOS moved to quell customer concerns, explicitly stating that no payment-card information or account passwords had been compromised during the incident. While the breach was limited to communication channels, it served as a stark reminder of the risks posed by reliance on third-party software vendors, which are increasingly becoming a vector for large-scale data leaks.
Simultaneously, the retail industry in France has been dealing with an entirely different and potentially more damaging type of threat. Over the night of October 11 and 12, a series of French supermarket chains were subjected to a sophisticated cyber-attack that targeted the very core of their physical operations: refrigeration management systems. By tampering with the digital controls responsible for maintaining safe temperatures for perishable goods, the attackers forced the retailers to discard a massive volume of food inventory.
The financial repercussions of the French attack are significant, with preliminary estimates placing the losses in the hundreds of thousands of euros. This incident represents a shift in the threat landscape, moving beyond the theft of customer credit card data to the direct sabotage of physical infrastructure—an evolution that poses a more immediate threat to the daily operational viability of brick-and-mortar retail.
The Growing Challenge of Digital Resilience
The confluence of these events—ranging from traditional network intrusions to the manipulation of industrial control systems—underscores a period of heightened risk for the retail sector. Large-scale retailers manage vast, interconnected digital ecosystems that include point-of-sale systems, supply chain logistics, customer loyalty databases, and, increasingly, Internet of Things (IoT) devices that govern physical store environments.
As companies move toward more integrated digital operations to improve efficiency and customer experience, they inadvertently expand their "attack surface." For firms like Ahold Delhaize and TFG, the immediate priority remains the restoration of services and the forensic analysis of their systems to identify how the breaches occurred. However, the broader retail industry is now facing a reckoning regarding the cost of security. The incidents observed this week suggest that "system separation"—the ability to isolate segments of a network so that a breach in one area does not bring down an entire global enterprise—is no longer a luxury, but a fundamental requirement for business continuity.
Regulatory bodies and cybersecurity agencies across Europe have long warned that retail, as a high-volume, data-rich industry, remains a primary target for organized cybercrime syndicates. The rapid succession of these incidents suggests that these threat actors are diversifying their tactics, testing everything from the robustness of peripheral third-party communication tools to the security of backend refrigeration controls.
As the investigations into Ahold Delhaize and TFG proceed, the retail community will likely look to these cases for lessons on incident response and containment. In the interim, retailers across the continent are expected to perform comprehensive audits of their security protocols, particularly those involving third-party integrations and internal network segmentation. While companies are currently navigating the immediate aftermath of these disruptions, the industry as a whole is bracing for a sustained period of volatility as digital threats continue to evolve in both frequency and sophistication. For the time being, there is no evidence to link the various incidents, yet the cumulative effect is a clear signal that the digital perimeter of modern retail is under unprecedented pressure.