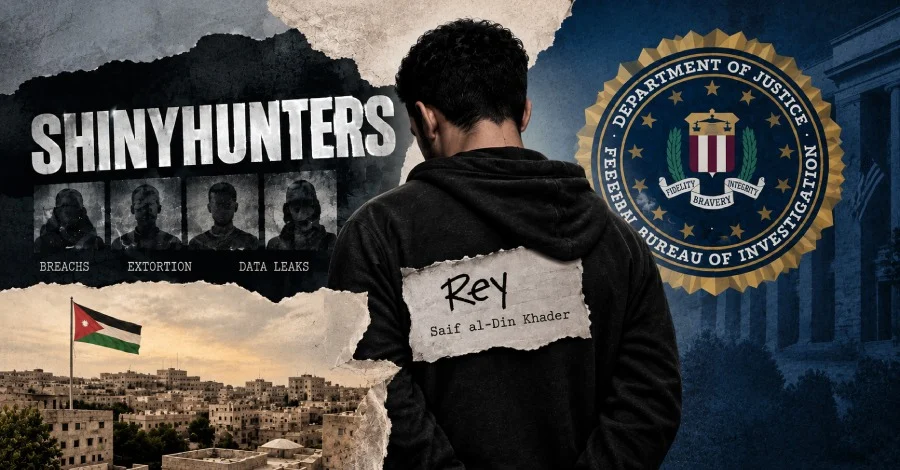
A suspected high-ranking member of the notorious ShinyHunters digital extortion collective, who operates under the online alias "Rey," has reportedly been detained by authorities in Jordan. According to reports citing sources familiar with the matter, the arrest marks a significant escalation in the international crackdown against one of the most prolific and aggressive cybercrime syndicates active in the modern threat landscape.
Rey, whose legal name is Saif-al-Din Khader and who has also gone by the moniker ReyXBF, was reportedly taken into custody on September 29, 2026. Following his detention, he has allegedly begun cooperating extensively with the U.S. Federal Bureau of Investigation (FBI) and regional law enforcement agencies to help identify and track down other core members of the decentralized hacking network.
"His cooperation is critical to ongoing efforts to arrest these hackers," a source close to the investigation told news agencies, highlighting the potential value of his inside perspective on the group’s operations.
Khader is far from an unknown entity within the cybersecurity research community. In a comprehensive threat intelligence report published in November 2025, independent security journalist Brian Krebs identified Rey as one of three primary administrators steering the Scattered LAPSUS$ Hunters (SLH or SLSH)—a dangerous amalgamation of actors historically tied to Scattered Spider, LAPSUS$, and ShinyHunters.
Krebs also noted at the time that Rey had previously served as an administrator for the data leak website associated with Hellcat, a disruptive ransomware group that emerged in late 2024. Furthermore, Khader took over as an administrator for the latest incarnation of BreachForums in 2024. Significantly, Khader had previously disclosed to Krebs that he had been cooperating with law enforcement officials since at least June 2025, suggesting a prolonged dual existence as an underground administrator and an informant.

This developing legal action against Khader forms part of a broader, coordinated multi-jurisdictional dragnet targeting the infrastructure and leadership of ShinyHunters. Just last week, Dutch police arrested a 24-year-old Amsterdam man for his alleged direct involvement in the threat actor’s malicious cyber operations. While official police channels withheld his identity, independent investigative reporting identified him as Pepijn van der Stap, a reformed hacker who had more recently been employed as an offensive security lead at the Dutch cybersecurity firm Neo Security. Following those reports, a designated spokesperson for ShinyHunters publicly denied maintaining any ongoing connections with van der Stap.
The recent arrests have prompted sharp public responses from high-ranking American law enforcement officials. Following the operation in Amsterdam, FBI Director Kash Patel took to social media to signal that the agency’s pressure campaign is intensifying. "FBI teams are actively working with partners to obtain and execute more leads in the ongoing investigation based on this arrest," Patel stated on X. In a subsequent post, he added, "FBI teams are working new leads RIGHT NOW. More arrests are on the table."
Over recent weeks, ShinyHunters has deliberately thrust itself into the global spotlight through a series of extraordinarily high-profile and disruptive cyber operations. Among them was a brazen operation to hijack the darknet website of a rival cybercriminal gang, Cl0p. The rival site takeover was achieved by exploiting an unpatched vulnerability in Grav CMS. Shortly thereafter, the group claimed responsibility for a stunning breach of the FBI’s official employment portal, "apply.fbijobs[.]gov," which allegedly resulted in the theft of approximately three terabytes of sensitive data.
Despite executing the FBI portal breach, ShinyHunters insisted that its primary motivation was not a monetary payoff or ransom extraction. Instead, the collective claimed the attack was designed to apply intense public and political pressure on the bureau, forcing it to amend what the group described as false allegations. Specifically, ShinyHunters sought to challenge law enforcement claims linking its operational core to "The Com," a notoriously loose-knit cybercrime collective associated with severe digital and physical offenses, including social engineering, phishing, SIM swapping, extortion, sextortion, swatting, kidnapping, and physical violence.
Law enforcement agencies, however, view the group through the lens of immense financial harm and widespread organizational disruption. Brett Leatherman, assistant director of the FBI’s cyber division, outlined the scale of the threat in a recorded statement detailing the collective’s activities.
"Since last year, this cybercriminal and his co-conspirators have allegedly breached more than 140 organizations and taken at least $70 million in extortion payments," Leatherman said. He explained that the syndicates frequently target third-party vendors operating within cloud-based platforms, weaponizing stolen sensitive data to extort corporate victims under the persistent threat of public publication.

Leatherman, who pointed to individuals like van der Stap as alleged leaders of the enterprise, also issued a direct warning to remaining members of the underground network. He emphasized that operatives can no longer safely hide behind perceived international anonymity or evade detection indefinitely.
"Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left. The longer you stay in this, the more we learn about you," Leatherman added. "You know how to find us, and we know how to find you. I suggest you reach out first while the choice is still yours."
Detailed historical analyses from cybersecurity firms Sekoia and Beazley Security trace the lineage and tactical evolution of ShinyHunters back to earlier progenitor hacking groups—namely TheDarkOverlord and GnosticPlayers—which specialized heavily in large-scale extortion and data leak operations. The ShinyHunters brand itself officially crystallized around April and May 2020, rising from the ashes of older underground forums.
Reflecting on the group’s surprising longevity, security researchers Enzo Saez and Robert (Bobby) Venal observed that the collective has transformed over the years.
"Six years on, ShinyHunters is less a group than a brand and business model that has outlived its founders," the researchers noted in a joint analysis. "What began in 2020 as a small crew trading stolen databases on RaidForums has become a persistent, self-renewing group that has absorbed indictments, arrests, and forum seizures without ever going quiet for long."
The researchers added that this remarkable resilience does not stem from any single charismatic leader or isolated operational cell. Rather, it derives from a modular division of labor: initial network access is procured by specialized social engineers, amplification and recruitment are handled by adjacent threat actors, and monetization is funneled under a shared, instantly recognizable brand name. As international law enforcement continues to unravel the network’s leadership through arrests and flipped informants, the durability of this decentralized business model faces its most severe test to date.